Average Ratings 0 Ratings
Average Ratings 0 Ratings
Similar Products
-
Astra PentestAstra's Pentest is a comprehensive solution for penetration testing. It includes an intelligent vulnerability scanner and in-depth manual pentesting. The automated scanner performs 10000+ security checks, including security checks for all CVEs listed in the OWASP top 10 and SANS 25. It also conducts all required tests to comply with ISO 27001 and HIPAA. Astra provides an interactive pentest dashboard which allows users to visualize vulnerability analysis, assign vulnerabilities to team members, collaborate with security experts, and to collaborate with security experts. The integrations with CI/CD platforms and Jira are also available if users don't wish to return to the dashboard each time they want to use it or assign a vulnerability for a team member.
-
csidec/side: The Client-Side Platform for Cybersecurity, Compliance, and Privacy Monitoring third-party scripts effectively eliminates uncertainty, ensuring that you are always aware of what is being delivered to your users' browsers, while also enhancing script performance by up to 30%. The unchecked presence of these scripts in users' browsers can lead to significant issues when things go awry, resulting in adverse publicity, potential legal actions, and claims for damages stemming from security breaches. Compliance with PCI DSS 4.0.1, particularly sections 6.4.3 and 11.6.1, requires that organizations handling cardholder data implement tamper-detection measures by March 31, 2025, to help prevent attacks by notifying stakeholders of unauthorized modifications to HTTP headers and payment information. c/side stands out as the sole fully autonomous detection solution dedicated to evaluating third-party scripts, moving beyond reliance on merely threat feed intelligence or easily bypassed detections. By leveraging historical data and artificial intelligence, c/side meticulously analyzes the payloads and behaviors of scripts, ensuring a proactive stance against emerging threats. Our continuous monitoring of numerous sites allows us to stay ahead of new attack vectors, as we process all scripts to refine and enhance our detection capabilities. This comprehensive approach not only safeguards your digital environment but also instills greater confidence in the security of third-party integrations.
-
Rocket z/Assure VAPYour mission-critical systems carry the weight of your entire organization. Protecting them shouldn't leave you guessing about hidden vulnerabilities or compliance risks. Rocket® z/Assure™ Vulnerability Analysis Program (VAP) is a specialized mainframe security solution built to proactively scan and safeguard your most valuable environments. By identifying system-level risks before they become active threats, we partner with you to ensure your infrastructure remains locked down, resilient, and fully compliant. We understand the responsibility of managing enterprise security, and our tool gives you the exact insights you need to confidently eliminate weak points. Key benefits for your security team: - Identify and resolve hidden vulnerabilities with deep, automated scanning. - Protect your mission-critical data from evolving external and internal threats. - Streamline compliance reporting with clear, actionable security insights. Take control of your mainframe security. Partner with Rocket Software to protect your digital foundation today.
-
Bitdefender Ultimate Small Business SecurityBitdefender Small Business Security provides robust, enterprise-level cyber-defense tailored for smaller companies, ensuring protection across various platforms including Windows, macOS, iOS, and Android. With a centralized management system that is user-friendly, it allows organizations lacking dedicated IT personnel to efficiently implement and oversee their security measures from a single interface. The solution features a multi-layered approach to endpoint protection, incorporating machine learning, behavioral analysis, real-time monitoring, process termination, and rollback capabilities to safeguard against both known and emerging threats. Additionally, it includes ransomware prevention and remediation strategies that detect unusual encryption activities and facilitate file recovery from backups. Users are also protected against fileless attacks, with measures like memory and back-injection interference as well as script blocking. The software further enhances security by preventing phishing and fraud through the blocking of malicious websites and alerting users accordingly, while offering advanced exploit protection with real-time shields for common applications such as browsers, Office software, and Adobe Reader, thus ensuring all-encompassing endpoint security. This comprehensive suite of features makes it an ideal choice for small businesses seeking to fortify their cybersecurity defenses.
-
Criminal IP ASMCriminal IP's Attack Surface Management (ASM) is an intelligence-driven platform designed to continuously identify, catalog, and oversee all internet-connected assets linked to an organization, including overlooked and shadow resources, enabling teams to understand their actual external exposure from the perspective of potential attackers. This solution integrates automated asset detection with open-source intelligence (OSINT) methods, artificial intelligence enhancements, and sophisticated threat intelligence to reveal exposed hosts, domains, cloud services, IoT devices, and other internet-facing entry points, while also collecting evidence such as screenshots and metadata, and linking findings to known vulnerabilities and attacker techniques. By evaluating exposures through the lens of business relevance and risk, ASM emphasizes vulnerable elements and misconfigurations, providing instantaneous alerts and interactive dashboards that facilitate quicker investigations and remediation efforts. Furthermore, this comprehensive tool empowers organizations to proactively manage their security posture, ensuring that they remain vigilant against emerging threats.
-
Aikido SecurityAikido is the all-in-one security platform for development teams to secure their complete stack, from code to cloud. Aikido centralizes all code and cloud security scanners in one place. Aikido offers a range of powerful scanners including static code analysis (SAST), dynamic application security testing (DAST), container image scanning, and infrastructure-as-code (IaC) scanning. Aikido integrates AI-powered auto-fixing features, reducing manual work by automatically generating pull requests to resolve vulnerabilities and security issues. It also provides customizable alerts, real-time vulnerability monitoring, and runtime protection, enabling teams to secure their applications and infrastructure seamlessly.
-
PackageX OCR ScanningPackageX OCR API turns any smartphone into an incredibly powerful universal label scanner. It can read every bit of text, including barcodes, QR codes and other information on the label. Our OCR technology is the best in the industry. It uses proprietary algorithms and deep learning models to extract information from labels. Our OCR API has been trained using information from more than 10 million labels. This allows for the highest scanning accuracy in the market, at over 95%. Our technology can scan in low-light conditions and read labels from any angle. Create your own OCR scanner app to eliminate pen-and-paper inefficiencies. Our OCR scanner allows you to extract information from printed text or handwritten labels. Our OCR software is trained using multilingual label data extracted in over 40 countries. Detect and extract information from barcodes or QR codes.
-
Orca SecurityOrca Security is the pioneer of agentless cloud security that is trusted by hundreds of enterprises globally. Orca makes cloud security possible for enterprises moving to and scaling in the cloud with its patented SideScanning™ technology and Unified Data Model. The Orca Cloud Security Platform delivers the world's most comprehensive coverage and visibility of risks across AWS, Azure, Google Cloud and Kubernetes.
-
ApifyApify provides the infrastructure developers need to build, deploy, and monetize web automation tools. The platform centers on Apify Store, a marketplace featuring 10,000+ community-built Actors. These are serverless programs that scrape websites, automate browser tasks, and power AI agents. Developers create Actors using JavaScript, Python, or Crawlee (Apify's open-source crawling library), then publish them to the Store. When other users run your Actor, you earn money. Apify manages the infrastructure, handles payments, and processes monthly payouts to thousands of active developers. Apify Store offers ready-to-use solutions for common use cases: extracting data from Amazon, Google Maps, and social platforms; monitoring prices; generating leads; and much more. Under the hood, Actors automatically manage proxy rotation, CAPTCHA solving, JavaScript-heavy pages, and headless browser orchestration. The platform scales on demand with 99.95% uptime and maintains SOC2, GDPR, and CCPA compliance. For workflow automation, Apify connects to Zapier, Make, n8n, and LangChain. The platform also offers an MCP server, enabling AI assistants like Claude to discover and invoke Actors programmatically.
-
Nutrient SDKNutrient provides an extensive solution for all your PDF requirements, delivering tools that seamlessly operate PDF features across any platform. 1. SDK: Incorporate advanced PDF functionality into iOS, Android, Windows, web, or any cross-platform technology, supplying abilities like PDF viewing, annotation, collaboration, and beyond. 2. Libraries: Employ our powerful .NET and Java libraries to enhance your backend applications with batch processing of redactions and PDF forms, OCR'd scanned text, and PDF document editing, all directly from your application server. 3. Processor: Our agile PDF microservice, Processor, enables rapid generation of PDFs from HTML, including HTML forms, as well as Office-to-PDF conversions, OCR, redaction, and XFDF combining and exporting. 4. PDF API: Take advantage of our hosted PDF API to generate, convert, and alter PDF documents in your workflows. We handle the development and server management, freeing you up to concentrate on your business. At Nutrient, we're not just a tool; we're a committed ally in your success. Gain direct contact with our engineers for expert guidance, utilize comprehensive examples to simplify integration, and make the most of our top-tier documentation.
Description
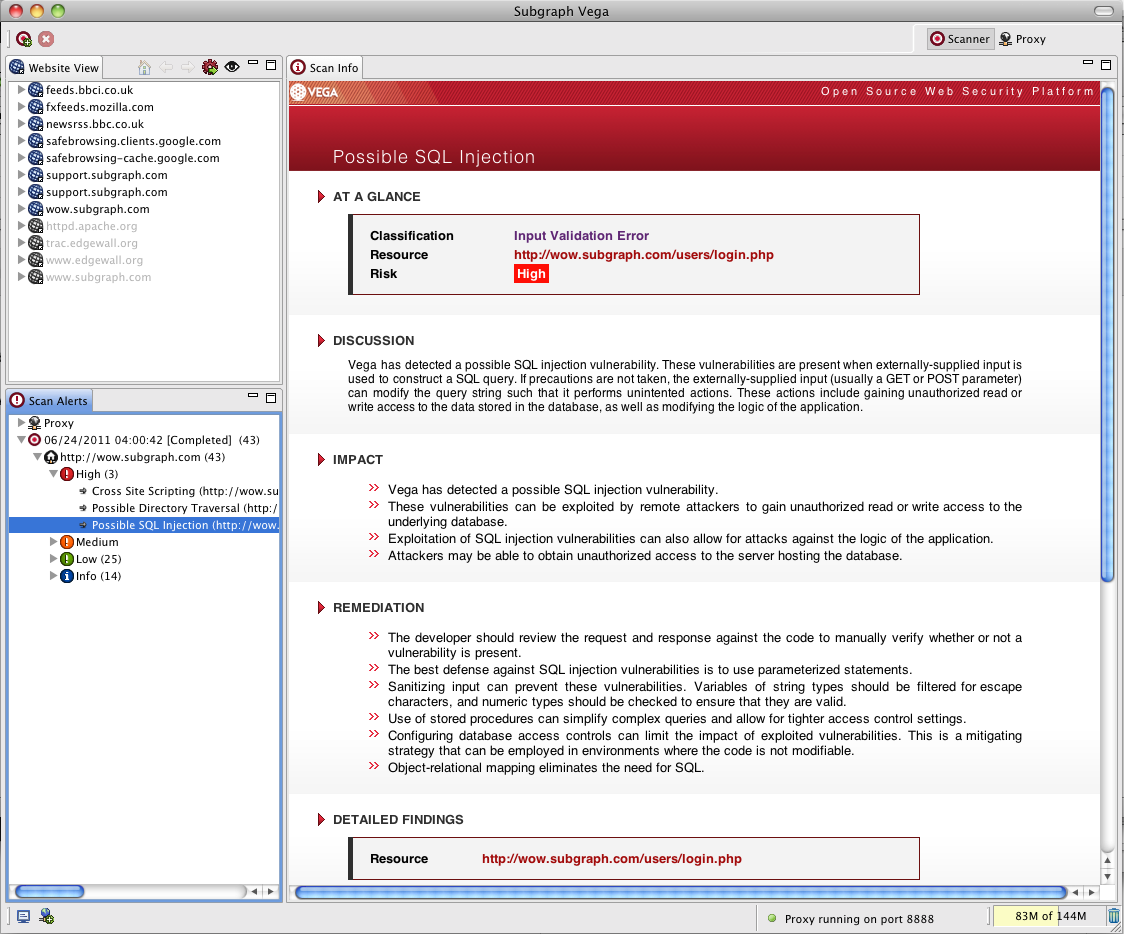
Vega is a powerful tool designed to assist in identifying and validating various security vulnerabilities, including SQL Injection, cross-site scripting, and the accidental exposure of sensitive data. This application, developed in Java, features a graphical user interface and is compatible with Linux, OS X, and Windows platforms. With Vega, you can detect a range of vulnerabilities like reflected and stored cross-site scripting, blind SQL injection, remote file inclusion, and shell injection, among others. Additionally, it assesses TLS/SSL security configurations and suggests enhancements for your TLS servers' security. The tool boasts an automated scanner for efficient testing and an intercepting proxy for in-depth analysis. Vega’s scanning capabilities are adept at uncovering SQL injection vulnerabilities and more. It also incorporates a website crawler to enhance its automated scanning process, and it has the ability to log into websites automatically when provided with user credentials. Overall, Vega is an invaluable resource for enhancing your web application's security posture.
Description
Garak evaluates the potential failures of an LLM in undesirable ways, examining aspects such as hallucination, data leakage, prompt injection, misinformation, toxicity, jailbreaks, and various other vulnerabilities. This free tool is designed with an eagerness for development, continually seeking to enhance its functionalities for better application support. Operating as a command-line utility, Garak is compatible with both Linux and OSX systems; you can easily download it from PyPI and get started right away. The pip version of Garak receives regular updates, ensuring it remains current, while its specific dependencies recommend setting it up within its own Conda environment. To initiate a scan, Garak requires the model to be analyzed and, by default, will conduct all available probes on that model utilizing the suggested vulnerability detectors for each. During the scanning process, users will see a progress bar for every loaded probe, and upon completion, Garak will provide a detailed evaluation of each probe's findings across all detectors. This makes Garak not only a powerful tool for assessment but also a vital resource for researchers and developers aiming to enhance the safety and reliability of LLMs.
API Access
Has API
No
API Access
Has API
No




Integrations
Cohere
No
Conda
No
Hugging Face
No
OpenAI
No
Replicate
No
Integrations
Cohere
Yes
Conda
Yes
Hugging Face
Yes
OpenAI
Yes
Replicate
Yes
Pricing Details
No price information available.
Free Trial
No
Free Version
No
Pricing Details
Free
Free Trial
No
Free Version
Yes
Deployment
Web-Based
No
On-Premises
No
iPhone App
No
iPad App
No
Android App
No
Windows
Yes
Mac
No
Linux
Yes
Chromebook
No
Deployment
Web-Based
No
On-Premises
No
iPhone App
No
iPad App
No
Android App
No
Windows
No
Mac
Yes
Linux
Yes
Chromebook
No
Customer Support
Business Hours
Yes
Live Rep (24/7)
No
Online Support
Yes
Customer Support
Business Hours
No
Live Rep (24/7)
No
Online Support
Yes
Types of Training
Training Docs
Yes
Webinars
No
Live Training (Online)
No
In Person
No
Types of Training
Training Docs
Yes
Webinars
No
Live Training (Online)
No
In Person
No
Vendor Details
Company Name
Subgraph
Founded
2010
Country
Canada
Website
subgraph.com/vega/
Vendor Details
Company Name
garak
Website
github.com/leondz/garak/
Product Features
Vulnerability Scanners
Asset Discovery
No
Black Box Scanning
No
Compliance Monitoring
No
Continuous Monitoring
No
Defect Tracking
No
Interactive Scanning
No
Logging and Reporting
No
Network Mapping
No
Perimeter Scanning
No
Risk Analysis
No
Threat Intelligence
No
Web Inspection
No
Product Features
Vulnerability Scanners
Asset Discovery
No
Black Box Scanning
No
Compliance Monitoring
No
Continuous Monitoring
No
Defect Tracking
No
Interactive Scanning
No
Logging and Reporting
No
Network Mapping
No
Perimeter Scanning
No
Risk Analysis
No
Threat Intelligence
No
Web Inspection
No
