Average Ratings 0 Ratings
Average Ratings 0 Ratings
Similar Products
-
Rocket z/Assure VAPYour mission-critical systems carry the weight of your entire organization. Protecting them shouldn't leave you guessing about hidden vulnerabilities or compliance risks. Rocket® z/Assure™ Vulnerability Analysis Program (VAP) is a specialized mainframe security solution built to proactively scan and safeguard your most valuable environments. By identifying system-level risks before they become active threats, we partner with you to ensure your infrastructure remains locked down, resilient, and fully compliant. We understand the responsibility of managing enterprise security, and our tool gives you the exact insights you need to confidently eliminate weak points. Key benefits for your security team: - Identify and resolve hidden vulnerabilities with deep, automated scanning. - Protect your mission-critical data from evolving external and internal threats. - Streamline compliance reporting with clear, actionable security insights. Take control of your mainframe security. Partner with Rocket Software to protect your digital foundation today.
-
Aikido SecurityAikido is the all-in-one security platform for development teams to secure their complete stack, from code to cloud. Aikido centralizes all code and cloud security scanners in one place. Aikido offers a range of powerful scanners including static code analysis (SAST), dynamic application security testing (DAST), container image scanning, and infrastructure-as-code (IaC) scanning. Aikido integrates AI-powered auto-fixing features, reducing manual work by automatically generating pull requests to resolve vulnerabilities and security issues. It also provides customizable alerts, real-time vulnerability monitoring, and runtime protection, enabling teams to secure their applications and infrastructure seamlessly.
-
JetBrains JunieJetBrains Junie is an innovative AI coding assistant that works inside many JetBrains IDEs to streamline programming efforts and boost efficiency. This agent leverages advanced AI to help developers write, test, and inspect code without leaving their familiar development environment. Junie offers both code execution and interactive collaboration, allowing programmers to switch between automated code writing and brainstorming sessions for features and improvements. By deeply understanding the codebase, Junie identifies the best ways to tackle tasks and ensures all changes meet quality standards through syntax and semantic checks. It also runs tests to minimize errors and keep the project healthy, freeing developers from routine tasks. Many developers have successfully built complex applications and games using Junie, highlighting its flexibility across different languages and frameworks. The AI adapts to each task’s complexity and workflow, making coding less tedious and more focused on creativity. Whether you are building a simple web app or a complex game, Junie offers smart support throughout the development cycle.
-
Criminal IP ASMCriminal IP's Attack Surface Management (ASM) is an intelligence-driven platform designed to continuously identify, catalog, and oversee all internet-connected assets linked to an organization, including overlooked and shadow resources, enabling teams to understand their actual external exposure from the perspective of potential attackers. This solution integrates automated asset detection with open-source intelligence (OSINT) methods, artificial intelligence enhancements, and sophisticated threat intelligence to reveal exposed hosts, domains, cloud services, IoT devices, and other internet-facing entry points, while also collecting evidence such as screenshots and metadata, and linking findings to known vulnerabilities and attacker techniques. By evaluating exposures through the lens of business relevance and risk, ASM emphasizes vulnerable elements and misconfigurations, providing instantaneous alerts and interactive dashboards that facilitate quicker investigations and remediation efforts. Furthermore, this comprehensive tool empowers organizations to proactively manage their security posture, ensuring that they remain vigilant against emerging threats.
-
NMI PaymentsNMI Payments gives developers, SaaS builders, ISVs and ISOs a simple path to embedded payments. As a full-stack processor, acquirer, and technology partner, NMI enables you to integrate, brand, and manage payment acceptance within your platform—without becoming a PayFac or building complex infrastructure. The platform combines flexibility, scalability, and speed, offering white-labeled payments infrastructure that keeps your brand front and center. With omnichannel support for in-store, online, in-app, and unattended payments, you can deliver a consistent merchant experience across every touchpoint. NMI also manages onboarding, compliance, and risk, freeing your team to focus on innovation and customer growth. Developer-First Experience NMI’s developer-first environment puts full control in your hands. Build, test, and launch payments in a modern sandbox with clear documentation and ready-to-use code snippets. Guided onboarding flows and API recipes simplify integration, while low-code and no-code tools accelerate deployment. Business users can evaluate monetization options with instant revenue calculators and self-service sign-up. Whether you’re embedding payments for the first time or scaling across channels, NMI helps you go live faster, stay compliant, and grow with confidence
-
Orca SecurityOrca Security is the pioneer of agentless cloud security that is trusted by hundreds of enterprises globally. Orca makes cloud security possible for enterprises moving to and scaling in the cloud with its patented SideScanning™ technology and Unified Data Model. The Orca Cloud Security Platform delivers the world's most comprehensive coverage and visibility of risks across AWS, Azure, Google Cloud and Kubernetes.
-
Google AI StudioGoogle AI Studio is an all-in-one environment designed for building AI-first applications with Google’s latest models. It supports Gemini, Imagen, Veo, and Gemma, allowing developers to experiment across multiple modalities in one place. The platform emphasizes vibe coding, enabling users to describe what they want and let AI handle the technical heavy lifting. Developers can generate complete, production-ready apps using natural language instructions. One-click deployment makes it easy to move from prototype to live application. Google AI Studio includes a centralized dashboard for API keys, billing, and usage tracking. Detailed logs and rate-limit insights help teams operate efficiently. SDK support for Python, Node.js, and REST APIs ensures flexibility. Quickstart guides reduce onboarding time to minutes. Overall, Google AI Studio blends experimentation, vibe coding, and scalable production into a single workflow.
-
RetoolRetool is a modern AI-native application development platform designed to help teams build internal software quickly and efficiently. It enables users to create agents, workflows, dashboards, and full-stack apps using natural language prompts and visual tools. Retool connects directly to databases, APIs, vector stores, and AI models to ensure applications work seamlessly with existing systems. The platform allows teams to transform raw data into actionable tools such as dashboards, admin panels, and monitoring systems. With drag-and-drop UI building, code-level customization, and AI-assisted generation, Retool supports multiple development styles. Built-in workflows automate complex processes while maintaining auditability and security. Retool fits naturally into standard engineering stacks with support for CI/CD and version control. Enterprise-grade permissions and hosting options ensure sensitive data stays protected. Used by thousands of companies worldwide, Retool helps teams ship AI-powered software faster. It bridges the gap between idea and production with speed and control.
-
Astra PentestAstra's Pentest is a comprehensive solution for penetration testing. It includes an intelligent vulnerability scanner and in-depth manual pentesting. The automated scanner performs 10000+ security checks, including security checks for all CVEs listed in the OWASP top 10 and SANS 25. It also conducts all required tests to comply with ISO 27001 and HIPAA. Astra provides an interactive pentest dashboard which allows users to visualize vulnerability analysis, assign vulnerabilities to team members, collaborate with security experts, and to collaborate with security experts. The integrations with CI/CD platforms and Jira are also available if users don't wish to return to the dashboard each time they want to use it or assign a vulnerability for a team member.
-
GearsetGearset is a full‑featured Salesforce DevOps solution built for the enterprise, giving teams the tools to adopt best practices across every stage of the DevOps lifecycle. From metadata and CPQ deployments to CI/CD, testing, code analysis, sandbox seeding, backups, archiving, and observability, Gearset gives teams unmatched insight and control over their Salesforce workflows. Over 3,000 organizations — including names like McKesson and IBM — rely on Gearset to deliver with security and scale in mind. With advanced governance, detailed audit trails, SOX/ISO/HIPAA support, multi‑team pipelines, integrated security checks, and adherence to ISO 27001, SOC 2, GDPR, CCPA/CPRA, and HIPAA, Gearset combines enterprise‑ready compliance with rapid onboarding and an intuitive interface — all in one platform. Leading firms in finance, healthcare, and tech trust Gearset to power their DevOps initiatives without adding complexity.
Description
Rafter is a security scanning platform designed with developers in mind, enabling the identification and resolution of vulnerabilities in GitHub repositories through a simple click or command. Its integration is smooth via a web-based dashboard, command-line interface, or REST API, allowing for the scanning of JavaScript, TypeScript, and Python code to uncover various issues such as exposed API keys, SQL injection vulnerabilities, XSS flaws, insecure dependencies, hardcoded credentials, and weaknesses in authentication. The results are organized into three clear categories: “Errors,” “Warnings,” and “Improvements,” each providing in-depth explanations, specific code locations, remediation guidance, and formatted prompts that can be easily utilized in AI coding tools. Users can access findings in both JSON and Markdown formats, automate scans as part of CI/CD pipelines, and seamlessly integrate scan results into their existing workflows. Rafter’s flexible approach accommodates no-code, low-code, and full-code environments, ensuring that developers can implement proactive security measures early in the software development process, making it not only effortless but also scalable as project requirements grow. This adaptability allows teams to maintain a robust security posture while focusing on delivering high-quality software efficiently.
Description
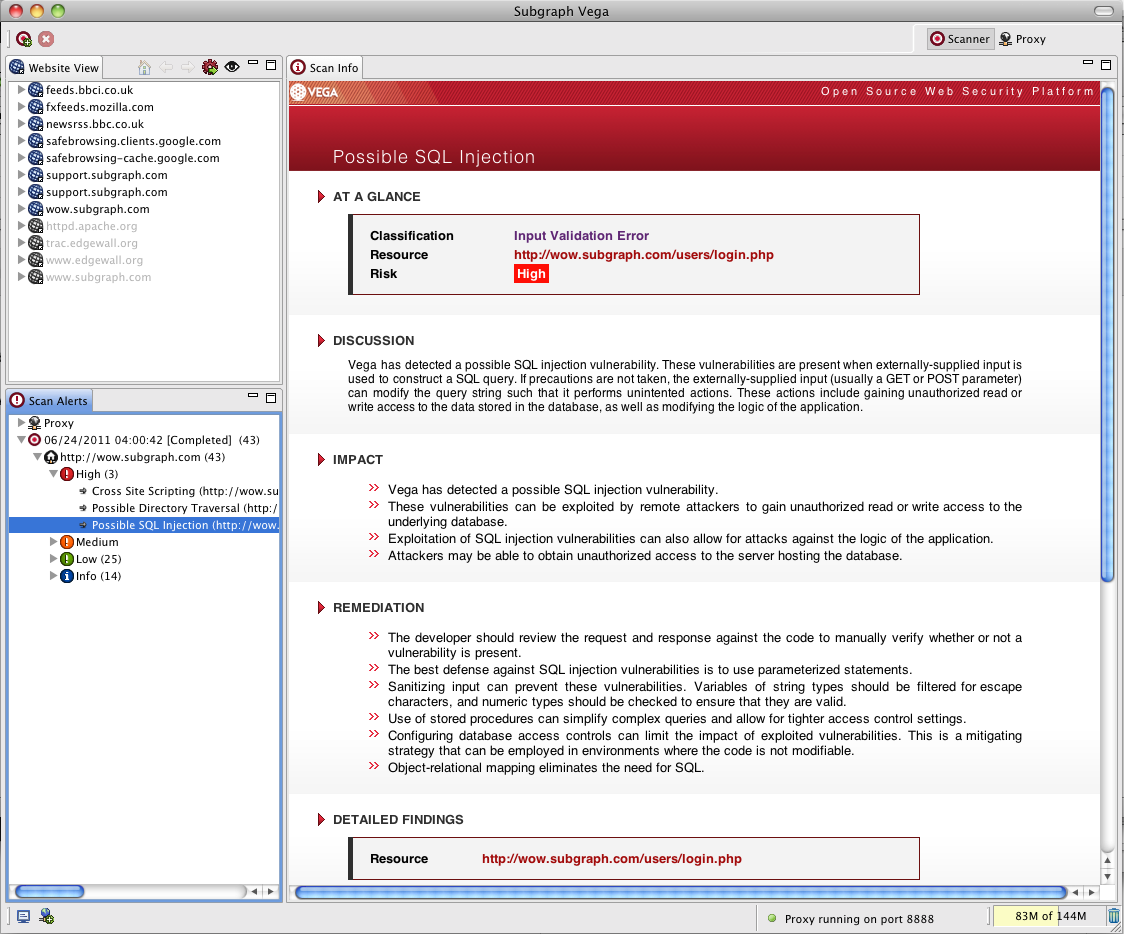
Vega is a powerful tool designed to assist in identifying and validating various security vulnerabilities, including SQL Injection, cross-site scripting, and the accidental exposure of sensitive data. This application, developed in Java, features a graphical user interface and is compatible with Linux, OS X, and Windows platforms. With Vega, you can detect a range of vulnerabilities like reflected and stored cross-site scripting, blind SQL injection, remote file inclusion, and shell injection, among others. Additionally, it assesses TLS/SSL security configurations and suggests enhancements for your TLS servers' security. The tool boasts an automated scanner for efficient testing and an intercepting proxy for in-depth analysis. Vega’s scanning capabilities are adept at uncovering SQL injection vulnerabilities and more. It also incorporates a website crawler to enhance its automated scanning process, and it has the ability to log into websites automatically when provided with user credentials. Overall, Vega is an invaluable resource for enhancing your web application's security posture.
API Access
Has API
Yes
API Access
Has API
No



Integrations
Git
Yes
GitHub
Yes
JSON
Yes
JavaScript
Yes
Markdown
Yes
Python
Yes
SQL
Yes
TypeScript
Yes
Integrations
Git
No
GitHub
No
JSON
No
JavaScript
No
Markdown
No
Python
No
SQL
No
TypeScript
No
Pricing Details
$39
Free Trial
No
Free Version
Yes
Pricing Details
No price information available.
Free Trial
No
Free Version
No
Deployment
Web-Based
Yes
On-Premises
No
iPhone App
No
iPad App
No
Android App
No
Windows
No
Mac
No
Linux
No
Chromebook
No
Deployment
Web-Based
No
On-Premises
No
iPhone App
No
iPad App
No
Android App
No
Windows
Yes
Mac
No
Linux
Yes
Chromebook
No
Customer Support
Business Hours
No
Live Rep (24/7)
No
Online Support
Yes
Customer Support
Business Hours
Yes
Live Rep (24/7)
No
Online Support
Yes
Types of Training
Training Docs
Yes
Webinars
No
Live Training (Online)
No
In Person
No
Types of Training
Training Docs
Yes
Webinars
No
Live Training (Online)
No
In Person
No
Vendor Details
Company Name
Rafter
Country
United States
Website
rafter.so/
Vendor Details
Company Name
Subgraph
Founded
2010
Country
Canada
Website
subgraph.com/vega/
Product Features
Vulnerability Scanners
Asset Discovery
No
Black Box Scanning
No
Compliance Monitoring
No
Continuous Monitoring
No
Defect Tracking
No
Interactive Scanning
No
Logging and Reporting
No
Network Mapping
No
Perimeter Scanning
No
Risk Analysis
No
Threat Intelligence
No
Web Inspection
No
Product Features
Vulnerability Scanners
Asset Discovery
No
Black Box Scanning
No
Compliance Monitoring
No
Continuous Monitoring
No
Defect Tracking
No
Interactive Scanning
No
Logging and Reporting
No
Network Mapping
No
Perimeter Scanning
No
Risk Analysis
No
Threat Intelligence
No
Web Inspection
No
