Average Ratings 0 Ratings
Average Ratings 0 Ratings
Similar Products
-
SOCRadar Extended Threat IntelligenceSOCRadar Extended Threat Intelligence is a holistic platform designed from the ground up to proactively detect and assess cyber threats, providing actionable insights with contextual relevance. Organizations increasingly require enhanced visibility into their publicly accessible assets and the vulnerabilities associated with them. Relying solely on External Attack Surface Management (EASM) solutions is inadequate for mitigating cyber risks; instead, these technologies should form part of a comprehensive enterprise vulnerability management framework. Companies are actively pursuing protection for their digital assets in every potential exposure area. The conventional focus on social media and the dark web no longer suffices, as threat actors continuously expand their methods of attack. Therefore, effective monitoring across diverse environments, including cloud storage and the dark web, is essential for empowering security teams. Additionally, for a thorough approach to Digital Risk Protection, it is crucial to incorporate services such as site takedown and automated remediation. This multifaceted strategy ensures that organizations remain resilient against the evolving landscape of cyber threats.
-
Criminal IPCriminal IP is a cyber threat intelligence search engine that detects vulnerabilities in personal and corporate cyber assets in real time and allows users to take preemptive actions. Coming from the idea that individuals and businesses would be able to boost their cyber security by obtaining information about accessing IP addresses in advance, Criminal IP's extensive data of over 4.2 billion IP addresses and counting to provide threat-relevant information about malicious IP addresses, malicious links, phishing websites, certificates, industrial control systems, IoTs, servers, CCTVs, etc. Using Criminal IP’s four key features (Asset Search, Domain Search, Exploit Search, and Image Search), you can search for IP risk scores and vulnerabilities related to searched IP addresses and domains, vulnerabilities for each service, and assets that are open to cyber attacks in image forms, in respective order.
-
ThreatLockerThreatLocker is a Zero Trust security platform that stops cyber threats by allowing only approved applications and activity to run. It removes standing admin rights, enforces least privilege, and gives organizations precise control over software behavior. With capabilities like application control, ringfencing, and device and storage restrictions, it prevents ransomware, zero day exploits, and unauthorized actions before they can execute. Purpose built for IT and security teams, ThreatLocker offers centralized management and full visibility across endpoints, users, and applications. It helps shrink the attack surface, restrict lateral movement, and meet compliance requirements with detailed auditing. Quick to deploy and easy to manage, the platform includes a large maintained application library and simplified approval workflows, enabling stronger security with less operational burden while keeping the business running smoothly.
-
Criminal IP ASMCriminal IP's Attack Surface Management (ASM) is an intelligence-driven platform designed to continuously identify, catalog, and oversee all internet-connected assets linked to an organization, including overlooked and shadow resources, enabling teams to understand their actual external exposure from the perspective of potential attackers. This solution integrates automated asset detection with open-source intelligence (OSINT) methods, artificial intelligence enhancements, and sophisticated threat intelligence to reveal exposed hosts, domains, cloud services, IoT devices, and other internet-facing entry points, while also collecting evidence such as screenshots and metadata, and linking findings to known vulnerabilities and attacker techniques. By evaluating exposures through the lens of business relevance and risk, ASM emphasizes vulnerable elements and misconfigurations, providing instantaneous alerts and interactive dashboards that facilitate quicker investigations and remediation efforts. Furthermore, this comprehensive tool empowers organizations to proactively manage their security posture, ensuring that they remain vigilant against emerging threats.
-
BranditScanBranditScan is an advanced platform utilizing artificial intelligence for safeguarding brands and monitoring online content, mainly serving digital creators and businesses to identify and eliminate unauthorized materials. This tool is particularly popular among content creators and influencers active on platforms like OnlyFans or Fansly, as it helps them fight against piracy and impersonation effectively. By leveraging this technology, users can maintain their brand integrity and ensure their work is protected from misuse.
-
PowerDMARCPowerDMARC is a robust email security solution that safeguards your brand reputation and email communications from threats like spoofing, phishing, and ransomware. By leveraging advanced technologies such as DMARC, SPF, DKIM, BIMI, MTA-STS, and TLS-RPT, PowerDMARC empowers you to protect your email infrastructure. With a user-friendly platform, PowerDMARC simplifies complex configurations, enabling you to easily manage and monitor your email security posture. AI-powered threat intelligence provides valuable insights to proactively identify and mitigate emerging threats. Trusted by over 2000 organizations globally, including Fortune 100 companies and governments, PowerDMARC is your trusted partner in securing your email infrastructure.
-
ESET PROTECT AdvancedESET Protect Advanced offers a comprehensive cybersecurity solution for businesses of any size. It offers advanced endpoint security against ransomware and zero-day threats. It also includes full disk encryption to ensure legal compliance and data security. The solution uses adaptive scanning, cloud sandboxing and behavioral analysis for proactive cloud-based threats defense. Mobile threat protection secures Android and iOS with anti-malware and anti-theft. It also offers cloud app security, mail server protection, vulnerability and patch management, and cloud app protection. Multi-factor authentication and extended detection and reaction (XDR) improve threat detection and response. The solution provides a single pane of glass remote management to provide visibility into threats and users. It also offers advanced reporting and customized notifications.
-
Bitdefender Ultimate Small Business SecurityBitdefender Small Business Security provides robust, enterprise-level cyber-defense tailored for smaller companies, ensuring protection across various platforms including Windows, macOS, iOS, and Android. With a centralized management system that is user-friendly, it allows organizations lacking dedicated IT personnel to efficiently implement and oversee their security measures from a single interface. The solution features a multi-layered approach to endpoint protection, incorporating machine learning, behavioral analysis, real-time monitoring, process termination, and rollback capabilities to safeguard against both known and emerging threats. Additionally, it includes ransomware prevention and remediation strategies that detect unusual encryption activities and facilitate file recovery from backups. Users are also protected against fileless attacks, with measures like memory and back-injection interference as well as script blocking. The software further enhances security by preventing phishing and fraud through the blocking of malicious websites and alerting users accordingly, while offering advanced exploit protection with real-time shields for common applications such as browsers, Office software, and Adobe Reader, thus ensuring all-encompassing endpoint security. This comprehensive suite of features makes it an ideal choice for small businesses seeking to fortify their cybersecurity defenses.
-
LeakCheckTake control of your cybersecurity and safeguard your credentials with ASCOMP LeakCheck. This privacy-focused Windows application allows you to verify if your email addresses and passwords have been compromised in historical data leaks, performing all checks securely right from your desktop. Security is the top priority: LeakCheck uses advanced k-anonymity technology. Your passwords are never transmitted in plain text; instead, encrypted hashes are used to safely query extensive breach databases. If any match is found, the software displays immediate warnings alongside detailed context, including the name, source, and date of the breach. With LeakCheck, you can proactively defend your online identity, pinpoint vulnerable accounts, and update compromised passwords before unauthorized users can exploit them.
-
JosysJosys is an AI-native identity security and governance platform built for the age of enterprise AI. As AI adoption accelerates, identity has become the fastest-growing attack surface and the hardest to govern. Josys discovers, governs, and secures every identity in the enterprise, human, machine, and AI agent, across every application. Its policy-led model lets security and IT teams set access policies once and enforce them autonomously: risk gets surfaced, access gets controlled, and identity threats get remediated in real time, with no manual oversight required. Over 1,000 organizations and MSPs worldwide trust Josys to turn identity from a liability into an autonomously governed advantage. Learn more at josys.com.
Description
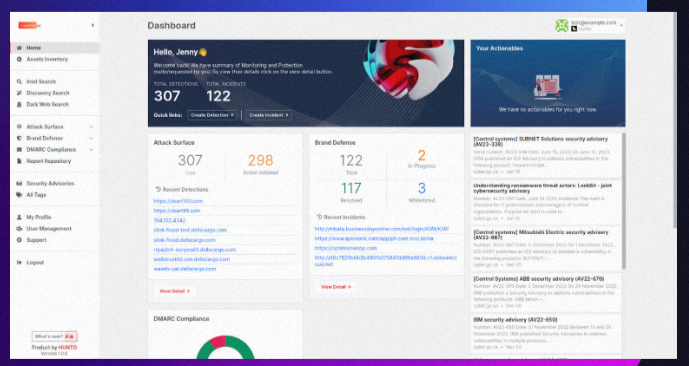
Our methodology ensures thorough life cycle defense against a wide variety of external dangers through a structured three-phase strategy encompassing discovery, monitoring, and enforcement. The skilled professionals on our team employ state-of-the-art algorithms combined with human insights to swiftly and precisely identify and address threats targeting your organization. By leveraging neural networks and sophisticated algorithms, our experts are able to proactively uncover potential threats aimed at your organization. Ongoing monitoring guarantees prompt reactions to emerging risks. By merging human intelligence with technological advancements, our security personnel effectively classify incidents as either benign or harmful, thereby refining threat evaluations. Experience a comprehensive defense against cyber threats with Hunto’s SaaS-based Digital Attack Surface Management (DASM) platform, designed for thorough protection. Additionally, our committed Security Operations Center (SOC) provides 24/7 surveillance, ensuring your organization remains consistently safeguarded against cyber threats. With such robust measures in place, you can focus on your core business activities with confidence.
Description
Wazuh is an open-source, enterprise-capable solution designed for security monitoring that effectively addresses threat detection, integrity monitoring, incident response, and compliance needs. By collecting, aggregating, indexing, and analyzing security data, Wazuh aids organizations in identifying intrusions, potential threats, and unusual behaviors. As cyber threats evolve in complexity, the demand for real-time monitoring and robust security analysis becomes increasingly critical for the swift detection and resolution of these threats. Our lightweight agent is equipped with essential monitoring and response functionalities, complemented by a server component that delivers security intelligence and performs comprehensive data analysis. Wazuh effectively meets the demand for ongoing monitoring and proactive responses to sophisticated threats, ensuring that security professionals have the necessary tools at their disposal. The platform emphasizes providing optimal visibility, offering valuable insights that empower security analysts to uncover, investigate, and address threats and attack strategies across a diverse range of endpoints. By integrating these features, Wazuh enhances an organization’s overall security posture.
API Access
Has API
No
API Access
Has API
No


Integrations
Abstract Security
No
Akitra Andromeda
No
Azure Marketplace
No
Criminal IP
No
Guardeon
No
HoneyWire
No
IVR Technology Group
No
JupiterOne
No
Observe
No
OctoXLabs
No
Integrations
Abstract Security
Yes
Akitra Andromeda
Yes
Azure Marketplace
Yes
Criminal IP
Yes
Guardeon
Yes
HoneyWire
Yes
IVR Technology Group
Yes
JupiterOne
Yes
Observe
Yes
OctoXLabs
Yes
Pricing Details
No price information available.
Free Trial
Yes
Free Version
No
Pricing Details
No price information available.
Free Trial
No
Free Version
No
Deployment
Web-Based
Yes
On-Premises
No
iPhone App
No
iPad App
No
Android App
No
Windows
No
Mac
No
Linux
No
Chromebook
No
Deployment
Web-Based
Yes
On-Premises
No
iPhone App
No
iPad App
No
Android App
No
Windows
No
Mac
No
Linux
No
Chromebook
No
Customer Support
Business Hours
Yes
Live Rep (24/7)
Yes
Online Support
Yes
Customer Support
Business Hours
Yes
Live Rep (24/7)
No
Online Support
Yes
Types of Training
Training Docs
Yes
Webinars
No
Live Training (Online)
Yes
In Person
Yes
Types of Training
Training Docs
Yes
Webinars
No
Live Training (Online)
No
In Person
No
Vendor Details
Company Name
Hunto.ai
Founded
2023
Country
Australia
Website
hunto.ai/
Vendor Details
Company Name
Wazuh
Founded
2015
Country
United States
Website
wazuh.com
Product Features
Brand Protection
Case Management
No
Domain Monitoring
No
Investigation Management
No
Marketplace Monitoring
No
Mobile App Monitoring
No
Paid Search Monitoring
No
Prioritization
No
Social Media Monitoring
No
Product Features
Endpoint Detection and Response (EDR)
Behavioral Analytics
No
Blacklisting/Whitelisting
No
Continuous Monitoring
No
Malware/Anomaly Detection
No
Prioritization
No
Remediation Management
No
Root Cause Analysis
No
Incident Response
Attack Behavior Analytics
No
Automated Remediation
No
Compliance Reporting
No
Forensic Data Retention
No
Incident Alerting
No
Incident Database
No
Incident Logs
No
Incident Reporting
No
Privacy Breach Reporting
No
SIEM Data Ingestion / Correlation
No
SLA Tracking / Management
No
Security Orchestration
No
Threat Intelligence
No
Timeline Analysis
No
Workflow Automation
No
Workflow Management
No
