Average Ratings 0 Ratings
Average Ratings 0 Ratings
Similar Products
-
ParasoftParasoft's mission is to provide automated testing solutions and expertise that empower organizations to expedite delivery of safe and reliable software. A powerful unified C and C++ test automation solution for static analysis, unit testing and structural code coverage, Parasoft C/C++test helps satisfy compliance with industry functional safety and security requirements for embedded software systems.
-
Checksum.aiEngineering teams shipping with AI have a new bottleneck: validation. Code output has accelerated. Quality hasn't. Checksum closes the gap. Checksum is a continuous quality platform with a suite of AI agents that handle testing end-to-end, at every stage of the development lifecycle. Where most tools wait for a human to trigger them, Checksum runs autonomously in the background, generating tests, executing them, and repairing failures without manual intervention. Seventy percent of test failures are resolved automatically through real-time auto-recovery. The platform covers every layer: end-to-end UI flows via Playwright, API endpoint chains, and targeted CI tests scoped to exactly what changed in a PR. All tests land as real code in your repository and are delivered as standard Playwright, owned by your team. Checksum is fine-tuned on 1.5+ million test runs and integrates natively with Cursor, Claude Code, and 100+ AI coding agents. Type /checksum and your coding agent's output gets tested before it ever reaches review. Generation and healing happen on Checksum's cloud infrastructure which means no LLM tokens consumed, no local resources required. The result: test suites that stay green as the product evolves, fewer regressions reaching production, and release confidence that scales alongside AI output.
-
MuukTestYou know that you could be testing more to catch bugs earlier, but QA testing can take a lot of time, effort and resources to do it right. MuukTest can get growing engineering teams up to 95% coverage of end-to-end tests in just 3 months. Our QA experts create, manage, maintain, and update E2E tests on the MuukTest Platform for your web, API, and mobile apps at record speed. We begin exploratory and negative tests after achieving 100% regression coverage within 8 weeks to uncover bugs and increase coverage. The time you spend on development is reduced by managing your testing frameworks, scripts, libraries and maintenance. We also proactively identify flaky tests and false test results to ensure the accuracy of your tests. Early and frequent testing allows you to detect errors in the early stages your development lifecycle. This reduces the burden of technical debt later on.
-
Virtuoso QAVirtuoso QA is an AI-native test automation solution built to streamline and scale enterprise quality assurance processes. It allows users to author tests in natural language, making it accessible for both technical and non-technical team members. The platform leverages self-healing AI to automatically adapt to changes in applications, reducing test flakiness and maintenance overhead. With features like live authoring, real-time execution, and automated diagnostics, teams can quickly identify and resolve issues. Virtuoso QA supports continuous testing across multiple browsers, devices, and environments, ensuring comprehensive test coverage. It integrates seamlessly with popular tools such as Jira, Jenkins, Azure DevOps, and BrowserStack, enabling smooth CI/CD workflows. The platform also provides detailed analytics and dashboards to track performance and optimize testing strategies. By automating test generation and execution, it significantly reduces manual effort and accelerates release cycles. Virtuoso QA empowers organizations to deliver high-quality software faster and more reliably.
-
QA WolfQA Wolf helps engineering teams achieve 80% automated test coverage end-to-end in just four months. Here's an overview of what you get in the box, whether it's 100 or 100,000 tests. • Automated end-to-end testing for 80% of the user flows in 4 months. The tests are written in Playwright, an open-source tool (no vendor lock-in; you own the code). • Test matrix and outline in the AAA framework. • Unlimited parallel testing on any environment of your choice. • We host and maintain 100% parallel-run infrastructure. • Maintenance of flaky and broken test for 24 hours. • Guaranteed 100% reliable results -- zero flakes. • Human-verified bugs sent via your messaging app as a bug report. • CI/CD Integration with your deployment pipelines and issue trackers. • Access to full-time QA Engineers at QA Wolf 24 hours a day.
-
GearsetGearset is a full‑featured Salesforce DevOps solution built for the enterprise, giving teams the tools to adopt best practices across every stage of the DevOps lifecycle. From metadata and CPQ deployments to CI/CD, testing, code analysis, sandbox seeding, backups, archiving, and observability, Gearset gives teams unmatched insight and control over their Salesforce workflows. Over 3,000 organizations — including names like McKesson and IBM — rely on Gearset to deliver with security and scale in mind. With advanced governance, detailed audit trails, SOX/ISO/HIPAA support, multi‑team pipelines, integrated security checks, and adherence to ISO 27001, SOC 2, GDPR, CCPA/CPRA, and HIPAA, Gearset combines enterprise‑ready compliance with rapid onboarding and an intuitive interface — all in one platform. Leading firms in finance, healthcare, and tech trust Gearset to power their DevOps initiatives without adding complexity.
-
Astra PentestAstra's Pentest is a comprehensive solution for penetration testing. It includes an intelligent vulnerability scanner and in-depth manual pentesting. The automated scanner performs 10000+ security checks, including security checks for all CVEs listed in the OWASP top 10 and SANS 25. It also conducts all required tests to comply with ISO 27001 and HIPAA. Astra provides an interactive pentest dashboard which allows users to visualize vulnerability analysis, assign vulnerabilities to team members, collaborate with security experts, and to collaborate with security experts. The integrations with CI/CD platforms and Jira are also available if users don't wish to return to the dashboard each time they want to use it or assign a vulnerability for a team member.
-
SynapSynap is an intelligent online exam platform for secure, question-based learning, trusted by organisations worldwide. Designed to help businesses, training providers, and educational institutions create, deliver, and manage both practice and high-stakes exams with ease. Synap offers a fully customisable, brandable portal, allowing companies to maintain their identity while providing seamless exam experiences. Our platform supports diverse question types including images, MCQs, and EMQs, which can be created directly or imported in bulk via CSV to streamline large-scale assessment needs. Integrated proctoring ensures exam integrity by monitoring candidates during live exams, preventing cheating and fraud. Synap delivers robust analytics and reporting tools, giving organisations detailed insights into learner performance, progress, and question effectiveness. This data empowers businesses to make informed decisions, improve training outcomes, and identify skill gaps quickly. With flexible exam timers, question randomisation, and secure environments, Synap scales effortlessly from small teams to enterprise-level clients. Plus, easy LMS integrations and API support enable smooth workflow automation. Synap’s intuitive interface requires minimal training, enabling organisations to deploy exams quickly and efficiently. Our dedicated customer success team provides ongoing support to ensure smooth implementation and continuous optimisation. Synap also supports compliance with data protection regulations, giving organisations peace of mind when handling sensitive learner data.
-
Rocket z/Assure VAPYour mission-critical systems carry the weight of your entire organization. Protecting them shouldn't leave you guessing about hidden vulnerabilities or compliance risks. Rocket® z/Assure™ Vulnerability Analysis Program (VAP) is a specialized mainframe security solution built to proactively scan and safeguard your most valuable environments. By identifying system-level risks before they become active threats, we partner with you to ensure your infrastructure remains locked down, resilient, and fully compliant. We understand the responsibility of managing enterprise security, and our tool gives you the exact insights you need to confidently eliminate weak points. Key benefits for your security team: - Identify and resolve hidden vulnerabilities with deep, automated scanning. - Protect your mission-critical data from evolving external and internal threats. - Streamline compliance reporting with clear, actionable security insights. Take control of your mainframe security. Partner with Rocket Software to protect your digital foundation today.
-
Aikido SecurityAikido is the all-in-one security platform for development teams to secure their complete stack, from code to cloud. Aikido centralizes all code and cloud security scanners in one place. Aikido offers a range of powerful scanners including static code analysis (SAST), dynamic application security testing (DAST), container image scanning, and infrastructure-as-code (IaC) scanning. Aikido integrates AI-powered auto-fixing features, reducing manual work by automatically generating pull requests to resolve vulnerabilities and security issues. It also provides customizable alerts, real-time vulnerability monitoring, and runtime protection, enabling teams to secure their applications and infrastructure seamlessly.
Description
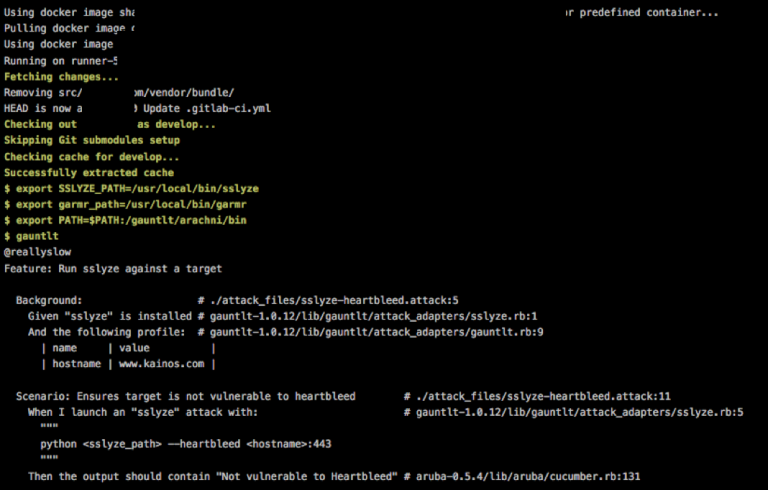
Gauntlt offers integrations with various security tools, enabling security, development, and operations teams to work together effectively in creating robust software. It is designed to enhance testing and foster communication among different teams, allowing for the creation of practical tests that can be incorporated into deployment and testing workflows. The attacks in Gauntlt are composed in a straightforward language that is easy to understand. It seamlessly integrates with your organization's existing testing tools and processes. Included with Gauntlt are security tool adapters that streamline the integration process. It utilizes standard error and standard output from Unix to communicate status updates. There are two primary methods for getting started with Gauntlt: you can either install it via the gem method, which requires you to download and configure the security tools (but rest assured, Gauntlt provides guidance throughout this process), or opt for the Gauntlt Starter Kit, a Vagrant script that automatically sets up the necessary tools for you. Traditionally, security testing occurs according to the auditors' timelines, and the resulting outputs often lack actionable insights, highlighting the need for more efficient solutions in security testing protocols. By using Gauntlt, teams can shift towards a more proactive and integrated approach to security testing, ultimately improving the overall security posture of their software projects.
Description
OpenText Dynamic Application Security Testing (DAST) offers enterprises a powerful, automated way to detect real-world security vulnerabilities by simulating live attacks against running applications, APIs, and services without requiring access to source code or staging environments. Tailored for DevSecOps teams, it efficiently prioritizes security issues to enable root cause analysis and faster remediation. The platform integrates effortlessly via REST APIs and features a user-friendly dashboard, supporting fully automated workflows within CI/CD pipelines for continuous security testing. OpenText DAST accelerates vulnerability discovery by tuning scans to the application environment, reducing false positives and surfacing critical risks earlier in the software development lifecycle. It supports modern web technologies including HTML5, JSON, AJAX, JavaScript, and HTTP2 to provide broad coverage across today’s digital applications. Automated features like macro generation and redundant page detection boost testing efficiency and reduce manual work. The solution offers flexible deployment choices, allowing organizations to operate on public or private clouds or on-premises systems. Backed by expert professional services, OpenText DAST helps businesses secure their software supply chains and maintain application integrity at scale.
API Access
Has API
No
API Access
Has API
Yes



Integrations
ArmorCode
No
Bizzy
No
Clarive
No
Conviso Platform
No
IRI FieldShield
No
Kondukto
No
SQUAD1
No
Seeker
No
ThreadFix
No
Integrations
ArmorCode
Yes
Bizzy
Yes
Clarive
Yes
Conviso Platform
Yes
IRI FieldShield
Yes
Kondukto
Yes
SQUAD1
Yes
Seeker
Yes
ThreadFix
Yes
Pricing Details
No price information available.
Free Trial
No
Free Version
Yes
Pricing Details
No price information available.
Free Trial
Yes
Free Version
No
Deployment
Web-Based
Yes
On-Premises
No
iPhone App
No
iPad App
No
Android App
No
Windows
No
Mac
No
Linux
No
Chromebook
No
Deployment
Web-Based
Yes
On-Premises
No
iPhone App
No
iPad App
No
Android App
No
Windows
No
Mac
No
Linux
No
Chromebook
No
Customer Support
Business Hours
No
Live Rep (24/7)
No
Online Support
Yes
Customer Support
Business Hours
No
Live Rep (24/7)
Yes
Online Support
Yes
Types of Training
Training Docs
Yes
Webinars
No
Live Training (Online)
Yes
In Person
No
Types of Training
Training Docs
Yes
Webinars
No
Live Training (Online)
No
In Person
No
Vendor Details
Company Name
Gauntlt
Website
gauntlt.org
Vendor Details
Company Name
OpenText
Founded
1991
Country
Canada
Website
www.opentext.com/products/dynamic-application-security-testing
Product Features
Automated Testing
Hierarchical View
No
Move & Copy
No
Parameterized Testing
No
Requirements-Based Testing
No
Security Testing
No
Supports Parallel Execution
No
Test Script Reviews
No
Unicode Compliance
No
Product Features
Application Security
Analytics / Reporting
No
Open Source Component Monitoring
No
Source Code Analysis
No
Third-Party Tools Integration
No
Training Resources
No
Vulnerability Detection
No
Vulnerability Remediation
No
