Average Ratings 0 Ratings
Average Ratings 0 Ratings
Similar Products
-
Aikido SecurityAikido is the all-in-one security platform for development teams to secure their complete stack, from code to cloud. Aikido centralizes all code and cloud security scanners in one place. Aikido offers a range of powerful scanners including static code analysis (SAST), dynamic application security testing (DAST), container image scanning, and infrastructure-as-code (IaC) scanning. Aikido integrates AI-powered auto-fixing features, reducing manual work by automatically generating pull requests to resolve vulnerabilities and security issues. It also provides customizable alerts, real-time vulnerability monitoring, and runtime protection, enabling teams to secure their applications and infrastructure seamlessly.
-
FerootFeroot Security is a global leader in AI-powered website and web application compliance and security. Feroot AI protects digital experiences from hidden threats while continuously enforcing compliance with PCI DSS 4.0.1, HIPAA rules on online tracking technologies, CCPA/CPRA, GDPR, CIPA, and over 50 global laws and standards. The Feroot AI Platform replaces manual compliance work and operational overhead with continuous automation. What once required months of effort across security, engineering, and legal teams can now be deployed in minutes, delivering real-time protection and audit-ready evidence. Feroot unifies critical capabilities into a single platform, including JavaScript behavior analysis, web compliance scanning, third-party script monitoring, consent enforcement, and data privacy posture management. It is purpose-built to detect and stop web-based threats such as Magecart, formjacking, e-skimming, and unauthorized tracking on high-risk assets like payment pages, login flows, iframes, and healthcare portals. Trusted by Fortune 500 enterprises, healthcare providers, retailers, SaaS platforms, utilities, payment service providers, universities, and public sector organizations, Feroot safeguards hundreds of millions of users worldwide. Feroot AI solutions include PaymentGuard AI, HealthData Shield AI, AlphaPrivacy AI, CodeGuard AI, and MobileGuard AI. Visit feroot for more information.
-
JscramblerJscrambler is the leader in Client-Side Security, protecting the code, data, and digital interactions that power today’s modern web applications. Modern applications are changing rapidly as development teams adopt AI-generated code, rely on third-party software components, and embed AI-powered agents into digital experiences. Meanwhile, sensitive information is increasingly created and processed in the browser itself. This creates a critical gap in enterprise security: organizations need to govern not only what code enters an application, but how that code, scripts, and data behave when the application runs. Jscrambler closes that gap with a Client-Side Security Platform built around its Behavioral Enforcement Core. The platform continuously monitors and enforces how application code, including AI-generated code, third-party scripts, AI agents, and sensitive data behave in the browser. By enforcing software integrity and data governance at runtime, Jscrambler gives organizations control at the point where code executes and data is created—before sensitive information can be exposed or transmitted. Organizations across retail, financial services, travel, healthcare, and other industries use Jscrambler to detect and stop client-side attacks, protect against risks introduced by AI-developed and third-party code, control AI-driven data flows, and strengthen compliance with requirements including PCI DSS, GDPR, HIPAA, CIPA, CCPA, and the EU AI Act.
-
WindocksWindocks provides on-demand Oracle, SQL Server, as well as other databases that can be customized for Dev, Test, Reporting, ML, DevOps, and DevOps. Windocks database orchestration allows for code-free end to end automated delivery. This includes masking, synthetic data, Git operations and access controls, as well as secrets management. Databases can be delivered to conventional instances, Kubernetes or Docker containers. Windocks can be installed on standard Linux or Windows servers in minutes. It can also run on any public cloud infrastructure or on-premise infrastructure. One VM can host up 50 concurrent database environments. When combined with Docker containers, enterprises often see a 5:1 reduction of lower-level database VMs.
-
Keeper SecurityPassword security is the foundation of cybersecurity. Keeper's powerful password security platform will protect your business from cyberthreats and data breaches related to passwords. Research shows that 81% of data breaches can be attributed to weak passwords. Password security platforms are an affordable and easy way for companies to address the root cause of most data breaches. Your business can significantly reduce the risk of data breaches by implementing Keeper. Keeper creates strong passwords for all websites and apps, then secures them on all devices. Each employee receives a private vault to store and manage their passwords, credentials and files, as well as private client data. Employees will save time and frustration by not having to remember, reset, reuse, or remember passwords. Industry compliance is achieved through strict and customizable role-based access controls. This includes 2FA, usage auditing, and event reporting.
-
Rocket z/Assure VAPYour mission-critical systems carry the weight of your entire organization. Protecting them shouldn't leave you guessing about hidden vulnerabilities or compliance risks. Rocket® z/Assure™ Vulnerability Analysis Program (VAP) is a specialized mainframe security solution built to proactively scan and safeguard your most valuable environments. By identifying system-level risks before they become active threats, we partner with you to ensure your infrastructure remains locked down, resilient, and fully compliant. We understand the responsibility of managing enterprise security, and our tool gives you the exact insights you need to confidently eliminate weak points. Key benefits for your security team: - Identify and resolve hidden vulnerabilities with deep, automated scanning. - Protect your mission-critical data from evolving external and internal threats. - Streamline compliance reporting with clear, actionable security insights. Take control of your mainframe security. Partner with Rocket Software to protect your digital foundation today.
-
Criminal IP ASMCriminal IP's Attack Surface Management (ASM) is an intelligence-driven platform designed to continuously identify, catalog, and oversee all internet-connected assets linked to an organization, including overlooked and shadow resources, enabling teams to understand their actual external exposure from the perspective of potential attackers. This solution integrates automated asset detection with open-source intelligence (OSINT) methods, artificial intelligence enhancements, and sophisticated threat intelligence to reveal exposed hosts, domains, cloud services, IoT devices, and other internet-facing entry points, while also collecting evidence such as screenshots and metadata, and linking findings to known vulnerabilities and attacker techniques. By evaluating exposures through the lens of business relevance and risk, ASM emphasizes vulnerable elements and misconfigurations, providing instantaneous alerts and interactive dashboards that facilitate quicker investigations and remediation efforts. Furthermore, this comprehensive tool empowers organizations to proactively manage their security posture, ensuring that they remain vigilant against emerging threats.
-
MaintainlyMaintainly is a cloud-hosted maintenance management solution that streamlines both proactive and reactive maintenance processes. This software enables users to generate, assign, and oversee work orders, offering features such as photo uploads, meter readings, downtime monitoring, and comprehensive audit trails, which can be handled either manually or through automated preventive schedules. Users can organize assets in a hierarchical manner, track movable equipment geographically, and utilize QR codes for easy access, while every maintenance activity is recorded in a detailed history log. Teams and technicians benefit from push notifications, and maintenance personnel can receive and monitor requests using a mobile application that includes functionalities for on-site updates, task comments, and tracking time spent on jobs. Maintainly also offers customizable hierarchy configurations, sophisticated filtering options, and role-specific views, enabling complex operations across various industries to expand efficiently. With a focus on user-friendly adoption, the platform boasts a quick setup process, scalable modular features, and an intuitive design that enhances the user experience. This combination of capabilities makes Maintainly a versatile tool for managing maintenance tasks effectively.
-
csidec/side: The Client-Side Platform for Cybersecurity, Compliance, and Privacy Monitoring third-party scripts effectively eliminates uncertainty, ensuring that you are always aware of what is being delivered to your users' browsers, while also enhancing script performance by up to 30%. The unchecked presence of these scripts in users' browsers can lead to significant issues when things go awry, resulting in adverse publicity, potential legal actions, and claims for damages stemming from security breaches. Compliance with PCI DSS 4.0.1, particularly sections 6.4.3 and 11.6.1, requires that organizations handling cardholder data implement tamper-detection measures by March 31, 2025, to help prevent attacks by notifying stakeholders of unauthorized modifications to HTTP headers and payment information. c/side stands out as the sole fully autonomous detection solution dedicated to evaluating third-party scripts, moving beyond reliance on merely threat feed intelligence or easily bypassed detections. By leveraging historical data and artificial intelligence, c/side meticulously analyzes the payloads and behaviors of scripts, ensuring a proactive stance against emerging threats. Our continuous monitoring of numerous sites allows us to stay ahead of new attack vectors, as we process all scripts to refine and enhance our detection capabilities. This comprehensive approach not only safeguards your digital environment but also instills greater confidence in the security of third-party integrations.
-
GoCodesTrack every tool, vehicle, and piece of equipment your team owns from a single account. GoCodes is asset tracking software built for contractors, manufacturers, and facilities teams. Each account includes customizable QR code labels at no extra cost. Scan them with the GoCodes mobile app (4.7 stars on the App Store) or any phone browser. Check-in and check-out takes seconds. Most teams are live within a week. Need more than QR? Add real-time GPS trackers, Bluetooth beacons, or RFID/NFC tags to the same platform. Four tracking technologies, one system. Schedule maintenance, log service history, and track warranties and utilization. Build custom reports, rename fields, add your own data points, and lock access with role-based permissions. GoCodes pairs cloud software, scanner apps, and rugged labels into one package. Start a free trial and see where your assets actually are.
Description
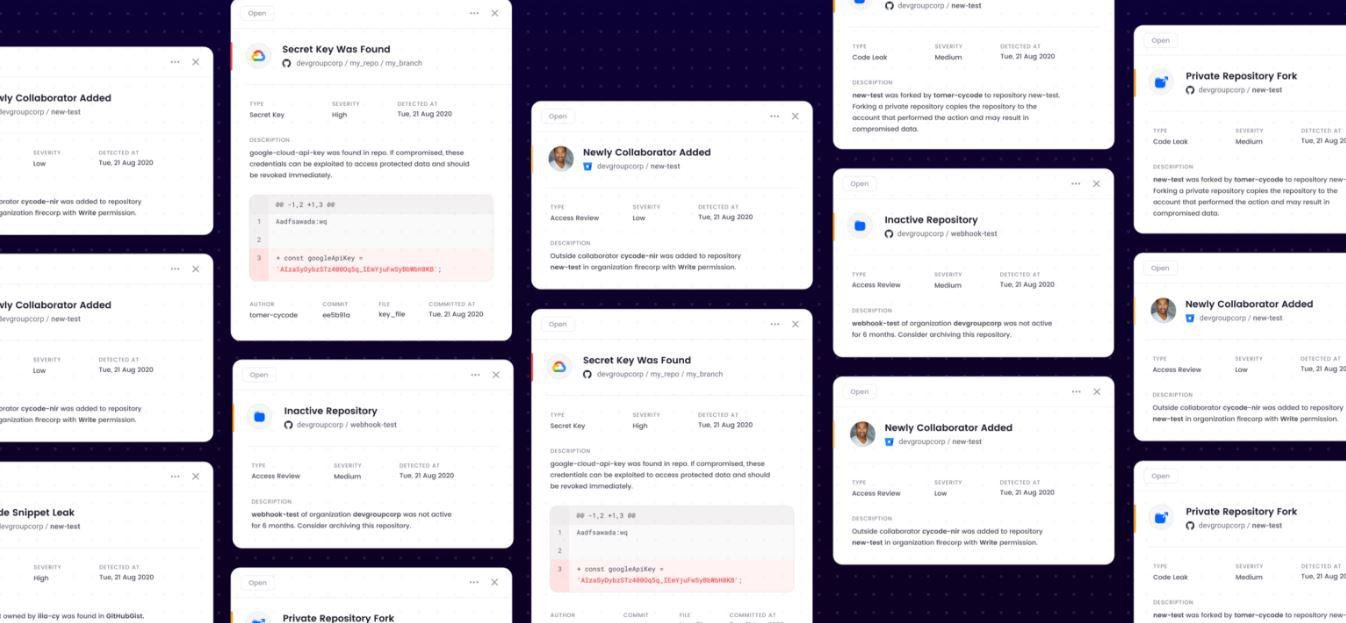
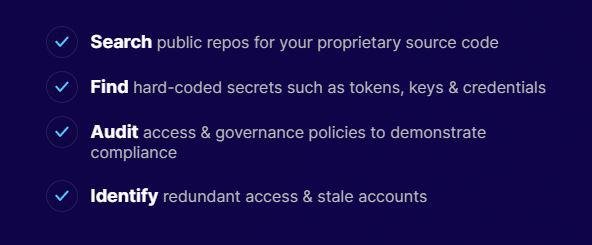
A comprehensive solution for ensuring security, governance, and pipeline integrity across all development tools and infrastructure is essential. Strengthen your source control management systems (SCM) by detecting secrets and leaks, while also safeguarding against code tampering. Examine your CI/CD configurations and Infrastructure-as-Code (IaC) for any security vulnerabilities or misconfigurations. Track any discrepancies between production systems’ IaC setups to thwart unauthorized code alterations. It's crucial to prevent developers from accidently making proprietary code public in repositories; this includes fingerprinting code assets and proactively identifying potential exposure on external sites. Maintain an inventory of assets, enforce stringent security policies, and easily showcase compliance throughout your DevOps ecosystem, whether it operates in the cloud or on-premises. Regularly scan IaC files for security flaws, ensuring alignment between specified IaC configurations and the actual infrastructure in use. Each commit or pull/merge request should be scrutinized for hard-coded secrets to prevent them from being merged into the master branch across all SCM platforms and various programming languages, thereby enhancing overall security measures. Implementing these strategies will create a robust security framework that supports both development agility and compliance.
Description
SaaS Security by Palo Alto Networks is a powerful, AI-driven platform that integrates seamlessly with SASE architecture to protect users, applications, and data across evolving SaaS landscapes. It tackles the growing challenges of shadow IT and generative AI apps, operational complexity, and the risk of sensitive data exposure. Using advanced machine learning, SaaS Security continuously discovers and categorizes SaaS and AI applications, extending visibility to entire AI ecosystems including copilot tools and plugins. The AI Access Security component safeguards enterprise data by monitoring and controlling both approved and shadow AI usage while preventing data leakage into unauthorized AI training. Its AI-powered data loss prevention covers multiple vectors including email and SaaS collaboration tools with high accuracy and fewer false positives. The solution automatically identifies and fixes misconfigurations, strengthens security posture, and simplifies policy enforcement. Inline machine learning stops zero-day threats in real time, and behavior analytics detect suspicious SaaS activities. All these capabilities are unified within a cloud-delivered console, enabling faster response and streamlined management.
API Access
Has API
No
API Access
Has API
No



Integrations
Amazon Web Services (AWS)
Yes
Axonius
Yes
CircleCI
Yes
Cobalt
Yes
Databricks
Yes
Flexport
Yes
GitHub
Yes
GitLab
Yes
Google Cloud Platform
Yes
Grubhub
Yes
Integrations
Amazon Web Services (AWS)
No
Axonius
No
CircleCI
No
Cobalt
No
Databricks
No
Flexport
No
GitHub
No
GitLab
No
Google Cloud Platform
No
Grubhub
No
Pricing Details
No price information available.
Free Trial
Yes
Free Version
No
Pricing Details
No price information available.
Free Trial
No
Free Version
No
Deployment
Web-Based
Yes
On-Premises
Yes
iPhone App
No
iPad App
No
Android App
No
Windows
No
Mac
No
Linux
No
Chromebook
No
Deployment
Web-Based
Yes
On-Premises
No
iPhone App
No
iPad App
No
Android App
No
Windows
No
Mac
No
Linux
No
Chromebook
No
Customer Support
Business Hours
No
Live Rep (24/7)
No
Online Support
Yes
Customer Support
Business Hours
No
Live Rep (24/7)
No
Online Support
Yes
Types of Training
Training Docs
Yes
Webinars
Yes
Live Training (Online)
Yes
In Person
No
Types of Training
Training Docs
Yes
Webinars
No
Live Training (Online)
No
In Person
No
Vendor Details
Company Name
Cycode
Founded
2019
Country
Israel
Website
cycode.com
Vendor Details
Company Name
Palo Alto Networks
Founded
2005
Country
United States
Website
www.paloaltonetworks.com
Product Features
Application Security
Analytics / Reporting
No
Open Source Component Monitoring
No
Source Code Analysis
No
Third-Party Tools Integration
No
Training Resources
No
Vulnerability Detection
No
Vulnerability Remediation
No
Cybersecurity
AI / Machine Learning
No
Behavioral Analytics
No
Endpoint Management
No
IOC Verification
No
Incident Management
No
Tokenization
No
Vulnerability Scanning
No
Whitelisting / Blacklisting
No
DevOps
Approval Workflow
No
Dashboard
No
KPIs
No
Policy Management
No
Portfolio Management
No
Prioritization
No
Release Management
No
Timeline Management
No
Troubleshooting Reports
No
