Average Ratings 0 Ratings
Average Ratings 0 Ratings
Similar Products
-
Aikido SecurityAikido is the all-in-one security platform for development teams to secure their complete stack, from code to cloud. Aikido centralizes all code and cloud security scanners in one place. Aikido offers a range of powerful scanners including static code analysis (SAST), dynamic application security testing (DAST), container image scanning, and infrastructure-as-code (IaC) scanning. Aikido integrates AI-powered auto-fixing features, reducing manual work by automatically generating pull requests to resolve vulnerabilities and security issues. It also provides customizable alerts, real-time vulnerability monitoring, and runtime protection, enabling teams to secure their applications and infrastructure seamlessly.
-
WindocksWindocks provides on-demand Oracle, SQL Server, as well as other databases that can be customized for Dev, Test, Reporting, ML, DevOps, and DevOps. Windocks database orchestration allows for code-free end to end automated delivery. This includes masking, synthetic data, Git operations and access controls, as well as secrets management. Databases can be delivered to conventional instances, Kubernetes or Docker containers. Windocks can be installed on standard Linux or Windows servers in minutes. It can also run on any public cloud infrastructure or on-premise infrastructure. One VM can host up 50 concurrent database environments. When combined with Docker containers, enterprises often see a 5:1 reduction of lower-level database VMs.
-
FerootFeroot Security is a global leader in AI-powered website and web application compliance and security. Feroot AI protects digital experiences from hidden threats while continuously enforcing compliance with PCI DSS 4.0.1, HIPAA rules on online tracking technologies, CCPA/CPRA, GDPR, CIPA, and over 50 global laws and standards. The Feroot AI Platform replaces manual compliance work and operational overhead with continuous automation. What once required months of effort across security, engineering, and legal teams can now be deployed in minutes, delivering real-time protection and audit-ready evidence. Feroot unifies critical capabilities into a single platform, including JavaScript behavior analysis, web compliance scanning, third-party script monitoring, consent enforcement, and data privacy posture management. It is purpose-built to detect and stop web-based threats such as Magecart, formjacking, e-skimming, and unauthorized tracking on high-risk assets like payment pages, login flows, iframes, and healthcare portals. Trusted by Fortune 500 enterprises, healthcare providers, retailers, SaaS platforms, utilities, payment service providers, universities, and public sector organizations, Feroot safeguards hundreds of millions of users worldwide. Feroot AI solutions include PaymentGuard AI, HealthData Shield AI, AlphaPrivacy AI, CodeGuard AI, and MobileGuard AI. Visit feroot for more information.
-
JscramblerJscrambler is the leader in Client-Side Security, protecting the code, data, and digital interactions that power today’s modern web applications. Modern applications are changing rapidly as development teams adopt AI-generated code, rely on third-party software components, and embed AI-powered agents into digital experiences. Meanwhile, sensitive information is increasingly created and processed in the browser itself. This creates a critical gap in enterprise security: organizations need to govern not only what code enters an application, but how that code, scripts, and data behave when the application runs. Jscrambler closes that gap with a Client-Side Security Platform built around its Behavioral Enforcement Core. The platform continuously monitors and enforces how application code, including AI-generated code, third-party scripts, AI agents, and sensitive data behave in the browser. By enforcing software integrity and data governance at runtime, Jscrambler gives organizations control at the point where code executes and data is created—before sensitive information can be exposed or transmitted. Organizations across retail, financial services, travel, healthcare, and other industries use Jscrambler to detect and stop client-side attacks, protect against risks introduced by AI-developed and third-party code, control AI-driven data flows, and strengthen compliance with requirements including PCI DSS, GDPR, HIPAA, CIPA, CCPA, and the EU AI Act.
-
GearsetGearset is a full‑featured Salesforce DevOps solution built for the enterprise, giving teams the tools to adopt best practices across every stage of the DevOps lifecycle. From metadata and CPQ deployments to CI/CD, testing, code analysis, sandbox seeding, backups, archiving, and observability, Gearset gives teams unmatched insight and control over their Salesforce workflows. Over 3,000 organizations — including names like McKesson and IBM — rely on Gearset to deliver with security and scale in mind. With advanced governance, detailed audit trails, SOX/ISO/HIPAA support, multi‑team pipelines, integrated security checks, and adherence to ISO 27001, SOC 2, GDPR, CCPA/CPRA, and HIPAA, Gearset combines enterprise‑ready compliance with rapid onboarding and an intuitive interface — all in one platform. Leading firms in finance, healthcare, and tech trust Gearset to power their DevOps initiatives without adding complexity.
-
Keeper SecurityPassword security is the foundation of cybersecurity. Keeper's powerful password security platform will protect your business from cyberthreats and data breaches related to passwords. Research shows that 81% of data breaches can be attributed to weak passwords. Password security platforms are an affordable and easy way for companies to address the root cause of most data breaches. Your business can significantly reduce the risk of data breaches by implementing Keeper. Keeper creates strong passwords for all websites and apps, then secures them on all devices. Each employee receives a private vault to store and manage their passwords, credentials and files, as well as private client data. Employees will save time and frustration by not having to remember, reset, reuse, or remember passwords. Industry compliance is achieved through strict and customizable role-based access controls. This includes 2FA, usage auditing, and event reporting.
-
JS7 JobSchedulerJS7 JobScheduler, an Open Source Workload Automation System, is designed for performance and resilience. JS7 implements state-of-the-art security standards. It offers unlimited performance for parallel executions of jobs and workflows. JS7 provides cross-platform job execution and managed file transfer. It supports complex dependencies without the need for coding. The JS7 REST-API allows automation of inventory management and job control. JS7 can operate thousands of Agents across any platform in parallel. Platforms - Cloud scheduling for Docker®, OpenShift®, Kubernetes® etc. - True multi-platform scheduling on premises, for Windows®, Linux®, AIX®, Solaris®, macOS® etc. - Hybrid cloud and on-premises use User Interface - Modern GUI with no-code approach for inventory management, monitoring, and control using web browsers - Near-real-time information provides immediate visibility to status changes, log outputs of jobs and workflows. - Multi-client functionality, role-based access management - OIDC authentication and LDAP integration High Availability - Redundancy & Resilience based on asynchronous design and autonomous Agents - Clustering of all JS7 Products, automatic fail-over and manual switch-over
-
Kasm WorkspacesKasm Workspaces streams your workplace environment directly to your web browser…on any device and from any location. Kasm is revolutionizing the way businesses deliver digital workspaces. We use our open-source web native container streaming technology to create a modern devops delivery of Desktop as a Service, application streaming, and browser isolation. Kasm is more than a service. It is a platform that is highly configurable and has a robust API that can be customized to your needs at any scale. Workspaces can be deployed wherever the work is. It can be deployed on-premise (including Air-Gapped Networks), in the cloud (Public and Private), or in a hybrid.
-
Rocket z/Assure VAPYour mission-critical systems carry the weight of your entire organization. Protecting them shouldn't leave you guessing about hidden vulnerabilities or compliance risks. Rocket® z/Assure™ Vulnerability Analysis Program (VAP) is a specialized mainframe security solution built to proactively scan and safeguard your most valuable environments. By identifying system-level risks before they become active threats, we partner with you to ensure your infrastructure remains locked down, resilient, and fully compliant. We understand the responsibility of managing enterprise security, and our tool gives you the exact insights you need to confidently eliminate weak points. Key benefits for your security team: - Identify and resolve hidden vulnerabilities with deep, automated scanning. - Protect your mission-critical data from evolving external and internal threats. - Streamline compliance reporting with clear, actionable security insights. Take control of your mainframe security. Partner with Rocket Software to protect your digital foundation today.
-
Criminal IP ASMCriminal IP's Attack Surface Management (ASM) is an intelligence-driven platform designed to continuously identify, catalog, and oversee all internet-connected assets linked to an organization, including overlooked and shadow resources, enabling teams to understand their actual external exposure from the perspective of potential attackers. This solution integrates automated asset detection with open-source intelligence (OSINT) methods, artificial intelligence enhancements, and sophisticated threat intelligence to reveal exposed hosts, domains, cloud services, IoT devices, and other internet-facing entry points, while also collecting evidence such as screenshots and metadata, and linking findings to known vulnerabilities and attacker techniques. By evaluating exposures through the lens of business relevance and risk, ASM emphasizes vulnerable elements and misconfigurations, providing instantaneous alerts and interactive dashboards that facilitate quicker investigations and remediation efforts. Furthermore, this comprehensive tool empowers organizations to proactively manage their security posture, ensuring that they remain vigilant against emerging threats.
Description
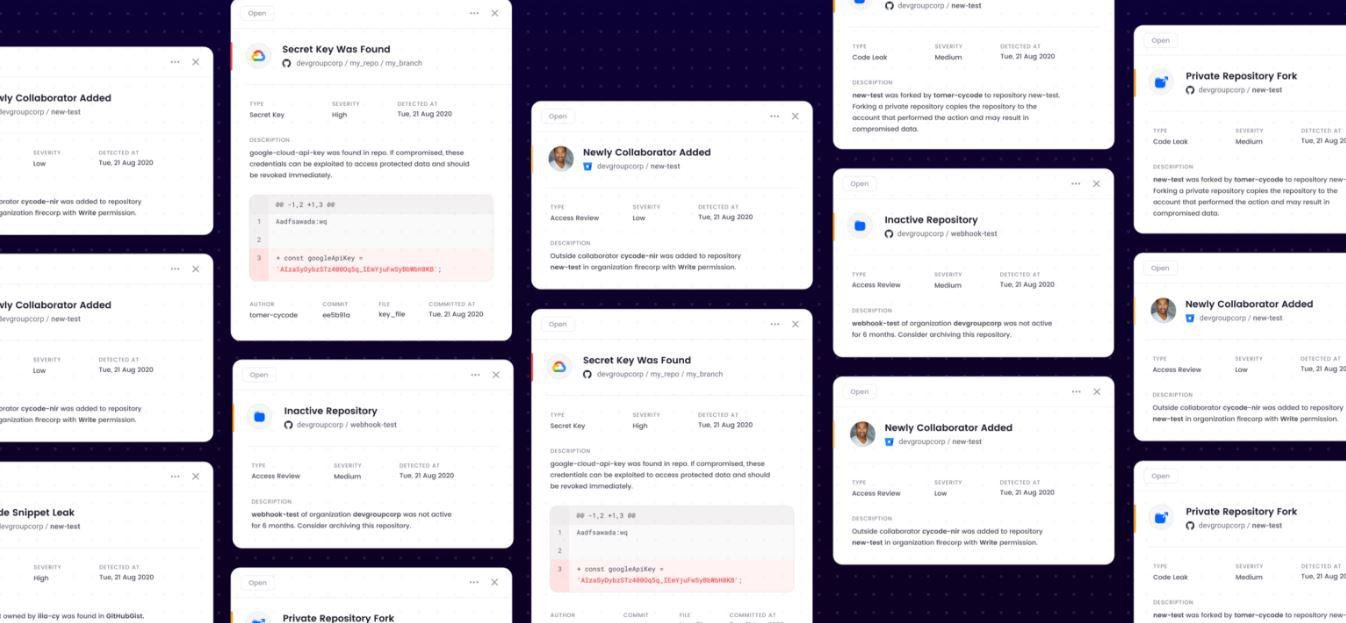
A comprehensive solution for ensuring security, governance, and pipeline integrity across all development tools and infrastructure is essential. Strengthen your source control management systems (SCM) by detecting secrets and leaks, while also safeguarding against code tampering. Examine your CI/CD configurations and Infrastructure-as-Code (IaC) for any security vulnerabilities or misconfigurations. Track any discrepancies between production systems’ IaC setups to thwart unauthorized code alterations. It's crucial to prevent developers from accidently making proprietary code public in repositories; this includes fingerprinting code assets and proactively identifying potential exposure on external sites. Maintain an inventory of assets, enforce stringent security policies, and easily showcase compliance throughout your DevOps ecosystem, whether it operates in the cloud or on-premises. Regularly scan IaC files for security flaws, ensuring alignment between specified IaC configurations and the actual infrastructure in use. Each commit or pull/merge request should be scrutinized for hard-coded secrets to prevent them from being merged into the master branch across all SCM platforms and various programming languages, thereby enhancing overall security measures. Implementing these strategies will create a robust security framework that supports both development agility and compliance.
Description
Rafter is a security scanning platform designed with developers in mind, enabling the identification and resolution of vulnerabilities in GitHub repositories through a simple click or command. Its integration is smooth via a web-based dashboard, command-line interface, or REST API, allowing for the scanning of JavaScript, TypeScript, and Python code to uncover various issues such as exposed API keys, SQL injection vulnerabilities, XSS flaws, insecure dependencies, hardcoded credentials, and weaknesses in authentication. The results are organized into three clear categories: “Errors,” “Warnings,” and “Improvements,” each providing in-depth explanations, specific code locations, remediation guidance, and formatted prompts that can be easily utilized in AI coding tools. Users can access findings in both JSON and Markdown formats, automate scans as part of CI/CD pipelines, and seamlessly integrate scan results into their existing workflows. Rafter’s flexible approach accommodates no-code, low-code, and full-code environments, ensuring that developers can implement proactive security measures early in the software development process, making it not only effortless but also scalable as project requirements grow. This adaptability allows teams to maintain a robust security posture while focusing on delivering high-quality software efficiently.
API Access
Has API
No
API Access
Has API
Yes



Integrations
GitHub
Yes
Amazon Web Services (AWS)
Yes
Axonius
Yes
CircleCI
Yes
Cobalt
Yes
Databricks
Yes
Flexport
Yes
GitLab
Yes
Google Cloud Platform
Yes
Grubhub
Yes
Integrations
GitHub
Yes
Amazon Web Services (AWS)
No
Axonius
No
CircleCI
No
Cobalt
No
Databricks
No
Flexport
No
GitLab
No
Google Cloud Platform
No
Grubhub
No
Pricing Details
No price information available.
Free Trial
Yes
Free Version
No
Pricing Details
$39
Free Trial
No
Free Version
Yes
Deployment
Web-Based
Yes
On-Premises
Yes
iPhone App
No
iPad App
No
Android App
No
Windows
No
Mac
No
Linux
No
Chromebook
No
Deployment
Web-Based
Yes
On-Premises
No
iPhone App
No
iPad App
No
Android App
No
Windows
No
Mac
No
Linux
No
Chromebook
No
Customer Support
Business Hours
No
Live Rep (24/7)
No
Online Support
Yes
Customer Support
Business Hours
No
Live Rep (24/7)
No
Online Support
Yes
Types of Training
Training Docs
Yes
Webinars
Yes
Live Training (Online)
Yes
In Person
No
Types of Training
Training Docs
Yes
Webinars
No
Live Training (Online)
No
In Person
No
Vendor Details
Company Name
Cycode
Founded
2019
Country
Israel
Website
cycode.com
Vendor Details
Company Name
Rafter
Country
United States
Website
rafter.so/
Product Features
Application Security
Analytics / Reporting
No
Open Source Component Monitoring
No
Source Code Analysis
No
Third-Party Tools Integration
No
Training Resources
No
Vulnerability Detection
No
Vulnerability Remediation
No
Cybersecurity
AI / Machine Learning
No
Behavioral Analytics
No
Endpoint Management
No
IOC Verification
No
Incident Management
No
Tokenization
No
Vulnerability Scanning
No
Whitelisting / Blacklisting
No
DevOps
Approval Workflow
No
Dashboard
No
KPIs
No
Policy Management
No
Portfolio Management
No
Prioritization
No
Release Management
No
Timeline Management
No
Troubleshooting Reports
No
Product Features
Vulnerability Scanners
Asset Discovery
No
Black Box Scanning
No
Compliance Monitoring
No
Continuous Monitoring
No
Defect Tracking
No
Interactive Scanning
No
Logging and Reporting
No
Network Mapping
No
Perimeter Scanning
No
Risk Analysis
No
Threat Intelligence
No
Web Inspection
No
