Average Ratings 0 Ratings
Average Ratings 0 Ratings
Similar Products
-
Aikido SecurityAikido is the all-in-one security platform for development teams to secure their complete stack, from code to cloud. Aikido centralizes all code and cloud security scanners in one place. Aikido offers a range of powerful scanners including static code analysis (SAST), dynamic application security testing (DAST), container image scanning, and infrastructure-as-code (IaC) scanning. Aikido integrates AI-powered auto-fixing features, reducing manual work by automatically generating pull requests to resolve vulnerabilities and security issues. It also provides customizable alerts, real-time vulnerability monitoring, and runtime protection, enabling teams to secure their applications and infrastructure seamlessly.
-
FerootFeroot Security is a global leader in AI-powered website and web application compliance and security. Feroot AI protects digital experiences from hidden threats while continuously enforcing compliance with PCI DSS 4.0.1, HIPAA rules on online tracking technologies, CCPA/CPRA, GDPR, CIPA, and over 50 global laws and standards. The Feroot AI Platform replaces manual compliance work and operational overhead with continuous automation. What once required months of effort across security, engineering, and legal teams can now be deployed in minutes, delivering real-time protection and audit-ready evidence. Feroot unifies critical capabilities into a single platform, including JavaScript behavior analysis, web compliance scanning, third-party script monitoring, consent enforcement, and data privacy posture management. It is purpose-built to detect and stop web-based threats such as Magecart, formjacking, e-skimming, and unauthorized tracking on high-risk assets like payment pages, login flows, iframes, and healthcare portals. Trusted by Fortune 500 enterprises, healthcare providers, retailers, SaaS platforms, utilities, payment service providers, universities, and public sector organizations, Feroot safeguards hundreds of millions of users worldwide. Feroot AI solutions include PaymentGuard AI, HealthData Shield AI, AlphaPrivacy AI, CodeGuard AI, and MobileGuard AI. Visit feroot for more information.
-
Rocket z/Assure VAPYour mission-critical systems carry the weight of your entire organization. Protecting them shouldn't leave you guessing about hidden vulnerabilities or compliance risks. Rocket® z/Assure™ Vulnerability Analysis Program (VAP) is a specialized mainframe security solution built to proactively scan and safeguard your most valuable environments. By identifying system-level risks before they become active threats, we partner with you to ensure your infrastructure remains locked down, resilient, and fully compliant. We understand the responsibility of managing enterprise security, and our tool gives you the exact insights you need to confidently eliminate weak points. Key benefits for your security team: - Identify and resolve hidden vulnerabilities with deep, automated scanning. - Protect your mission-critical data from evolving external and internal threats. - Streamline compliance reporting with clear, actionable security insights. Take control of your mainframe security. Partner with Rocket Software to protect your digital foundation today.
-
JscramblerJscrambler is the leader in Client-Side Security, protecting the code, data, and digital interactions that power today’s modern web applications. Modern applications are changing rapidly as development teams adopt AI-generated code, rely on third-party software components, and embed AI-powered agents into digital experiences. Meanwhile, sensitive information is increasingly created and processed in the browser itself. This creates a critical gap in enterprise security: organizations need to govern not only what code enters an application, but how that code, scripts, and data behave when the application runs. Jscrambler closes that gap with a Client-Side Security Platform built around its Behavioral Enforcement Core. The platform continuously monitors and enforces how application code, including AI-generated code, third-party scripts, AI agents, and sensitive data behave in the browser. By enforcing software integrity and data governance at runtime, Jscrambler gives organizations control at the point where code executes and data is created—before sensitive information can be exposed or transmitted. Organizations across retail, financial services, travel, healthcare, and other industries use Jscrambler to detect and stop client-side attacks, protect against risks introduced by AI-developed and third-party code, control AI-driven data flows, and strengthen compliance with requirements including PCI DSS, GDPR, HIPAA, CIPA, CCPA, and the EU AI Act.
-
Planview ProjectAdvantagePlanview ProjectAdvantage brings clarity, control, and scalability to enterprise project management by unifying project data, resources, and performance insights in one platform. Built for growing PMOs and complex organizations, it eliminates silos and inefficiencies by connecting teams through a single source of truth. Users can monitor resource allocation, track workloads, and forecast capacity with precision using dynamic dashboards. ProjectAdvantage’s portfolio scoring tools and sandbox environments make it easy to prioritize initiatives and align them with company strategy. Its flexibility supports any methodology—Agile, hybrid, or Waterfall—making it ideal for diverse industries and workflows. Seamless integrations with leading enterprise systems like Jira, ServiceNow, and Microsoft Teams enable cross-functional collaboration and real-time visibility. Backed by AI-driven analytics, Planview Projectadvantage helps accelerate project delivery, improve performance tracking, and ensure continuous strategic alignment. Designed for agility, it’s a transformative solution that turns project chaos into structured, measurable success.
-
RealCISORealCISO is a compliance intelligence platform for two audiences: MSPs and MSSPs managing security across multiple clients, and enterprise teams running compliance in-house. MSPs, MSSPs, and security consultants use it to run compliance assessments, manage cyber risk, track remediation, and report to boards — all in one place. Assessments map directly to NIST CSF, SOC 2, NIST 800-171, HIPAA, CIS Controls, CMMC, and 30+ other frameworks. Instead of months of spreadsheet work, clients get a clear picture of where they stand and what to fix — in days. Over 3,000 security providers rely on RealCISO to deliver vCISO services at scale. Built by practitioners. Founded by Brian Haugli — former DoD, former VP & CSO at The Hanover Insurance Group, CISSP, and co-author of the NIST CSF book published by Wiley.
-
Securden Unified PAMSecurden Unified PAM is a comprehensive solution designed for privileged access security, enabling users to identify, store, categorize, share, manage, and monitor all privileged accounts, passwords, keys, documents, and various identities. This tool establishes a centralized system for managing passwords, automates procedures through approval workflows, governs access permissions, tracks and logs all interactions with essential IT resources, and promotes adherence to password security protocols. The primary components of Securden Unified PAM include modules for password management, privileged account oversight, secure remote access, application governance, endpoint privilege regulation, management of privileged sessions, and SSH key administration. Additionally, the platform is aligned with numerous compliance standards such as NIS2, DORA, NIST, PCI-DSS, HIPAA, and ISO-IEC 27001, ensuring rigorous security measures. Installation is generally rapid, often completed in mere minutes, and organizations can expect to have a fully operational privileged access management system set up in under a month using Securden Unified PAM. Furthermore, this efficiency allows businesses to quickly enhance their security posture while minimizing disruptions to their ongoing operations.
-
Adaptive SecurityAdaptive Security is OpenAI’s investment for AI cyber threats. The company was founded in 2024 by serial entrepreneurs Brian Long and Andrew Jones. Adaptive has raised $50M+ from investors like OpenAI, a16z and executives at Google Cloud, Fidelity, Plaid, Shopify, and other leading companies. Adaptive protects customers from AI-powered cyber threats like deepfakes, vishing, smishing, and email spear phishing with its next-generation security awareness training and AI phishing simulation platform. With Adaptive, security teams can prepare employees for advanced threats with incredible, highly customized training content that is personalized for employee role and access levels, features open-source intelligence about their company, and includes amazing deepfakes of their own executives. Customers can measure the success of their training program over time with AI-powered phishing simulations. Hyper-realistic deepfake, voice, SMS, and email phishing tests assess risk levels across all threat vectors. Adaptive simulations are powered by an AI open-source intelligence engine that gives clients visibility into how their company's digital footprint can be leveraged by cybercriminals. Today, Adaptive’s customers include leading global organizations like Figma, The Dallas Mavericks, BMC Software, and Stone Point Capital. The company has a world class NPS score of 94, among the highest in cybersecurity.
-
Monitask🚀 Supercharge Your Team's Productivity! 🚀 Introducing the ultimate productivity hack for the modern workforce. Whether your squad is crushing it in the office, remote, or rocking that hybrid life, we've got you covered. 📊 What's in the box? Smart Time Tracking: Auto clock-in/out. No more "I forgot" excuses! Random Screenshots: Catch those Insta-scrolling moments Web Detective: Know if they're coding or... "coding" 😉 Real-time Mission Control: See who's winning at work Ninja Mode: Stealth monitoring for the win Perfect for: Startups, agencies, outsourcing pros, and corporate giants 💡 Why it's awesome: Turn productivity data into team superpowers Spot workflow kryptonite and zap it Keep it ethical: Privacy for employees, insights for you 🕵️ Ninja Mode: Psst! Our stealth feature lets you observe natural work habits. It's like having a productivity crystal ball! 🔒 Fort Knox-level security included. Because we're paranoid, so you don't have to be. Ready to transform your team into productivity superheroes? Let's go! 🦸♂️🦸♀️
-
SOCRadar Extended Threat IntelligenceSOCRadar Extended Threat Intelligence is a holistic platform designed from the ground up to proactively detect and assess cyber threats, providing actionable insights with contextual relevance. Organizations increasingly require enhanced visibility into their publicly accessible assets and the vulnerabilities associated with them. Relying solely on External Attack Surface Management (EASM) solutions is inadequate for mitigating cyber risks; instead, these technologies should form part of a comprehensive enterprise vulnerability management framework. Companies are actively pursuing protection for their digital assets in every potential exposure area. The conventional focus on social media and the dark web no longer suffices, as threat actors continuously expand their methods of attack. Therefore, effective monitoring across diverse environments, including cloud storage and the dark web, is essential for empowering security teams. Additionally, for a thorough approach to Digital Risk Protection, it is crucial to incorporate services such as site takedown and automated remediation. This multifaceted strategy ensures that organizations remain resilient against the evolving landscape of cyber threats.
Description
Achieve a thorough understanding of your application security landscape. Elevate the maturity of your secure development practices while minimizing the potential risks tied to your offerings. Application Security Posture Management (ASPM) tools are essential for the continuous oversight of application vulnerabilities, tackling security challenges from the initial development stages through to deployment. Development teams often face considerable hurdles, such as managing an expanding array of products and lacking a holistic perspective on vulnerabilities. We facilitate progress in maturity by assisting in the establishment of AppSec programs, overseeing the actions taken, monitoring key performance indicators, and more. By clearly defining requirements, processes, and policies, we empower security to be integrated early in the development cycle, thereby streamlining resources and time spent on additional testing or validations. This proactive approach ensures that security considerations are embedded throughout the entire lifecycle of the application.
Description
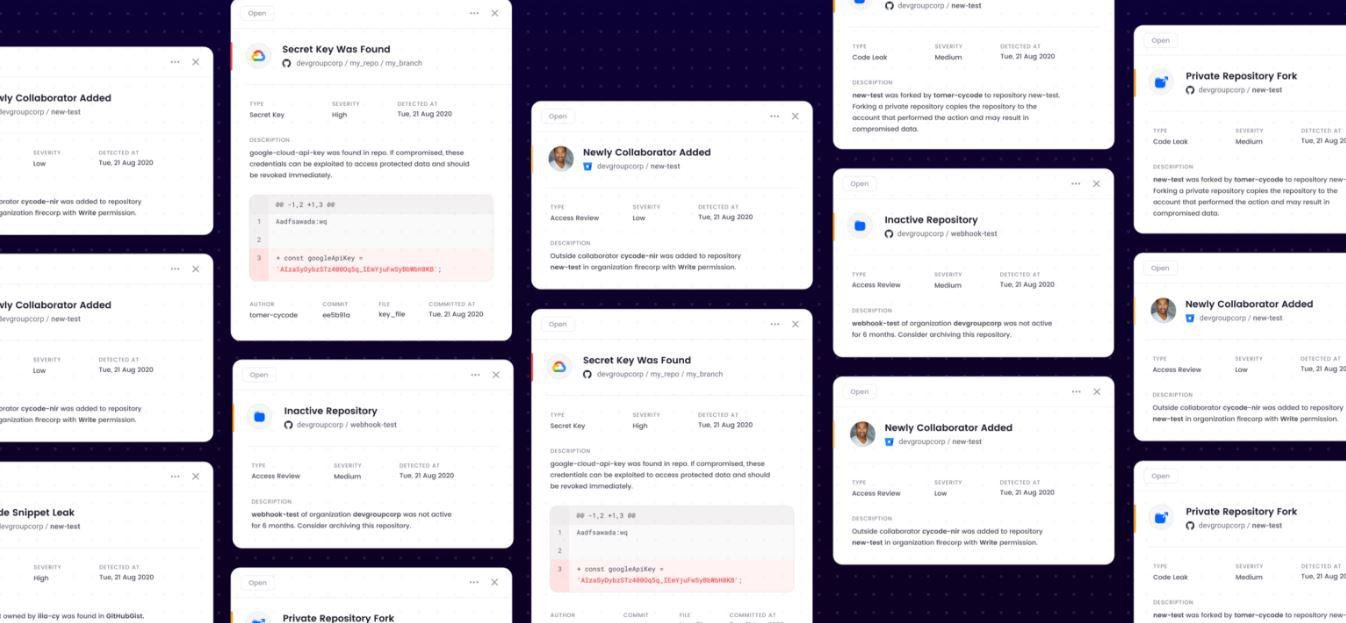
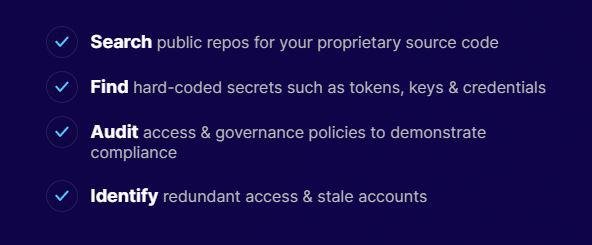
A comprehensive solution for ensuring security, governance, and pipeline integrity across all development tools and infrastructure is essential. Strengthen your source control management systems (SCM) by detecting secrets and leaks, while also safeguarding against code tampering. Examine your CI/CD configurations and Infrastructure-as-Code (IaC) for any security vulnerabilities or misconfigurations. Track any discrepancies between production systems’ IaC setups to thwart unauthorized code alterations. It's crucial to prevent developers from accidently making proprietary code public in repositories; this includes fingerprinting code assets and proactively identifying potential exposure on external sites. Maintain an inventory of assets, enforce stringent security policies, and easily showcase compliance throughout your DevOps ecosystem, whether it operates in the cloud or on-premises. Regularly scan IaC files for security flaws, ensuring alignment between specified IaC configurations and the actual infrastructure in use. Each commit or pull/merge request should be scrutinized for hard-coded secrets to prevent them from being merged into the master branch across all SCM platforms and various programming languages, thereby enhancing overall security measures. Implementing these strategies will create a robust security framework that supports both development agility and compliance.
API Access
Has API
Yes
API Access
Has API
No



Integrations
CircleCI
Yes
GitHub
Yes
Google Cloud Platform
Yes
Jenkins
Yes
Jira
Yes
Microsoft Azure
Yes
Slack
Yes
Amazon Web Services (AWS)
No
Axonius
No
Checkmarx
Yes
Integrations
CircleCI
Yes
GitHub
Yes
Google Cloud Platform
Yes
Jenkins
Yes
Jira
Yes
Microsoft Azure
Yes
Slack
Yes
Amazon Web Services (AWS)
Yes
Axonius
Yes
Checkmarx
No
Pricing Details
$20.99 per asset
Free Trial
No
Free Version
Yes
Pricing Details
No price information available.
Free Trial
Yes
Free Version
No
Deployment
Web-Based
Yes
On-Premises
No
iPhone App
No
iPad App
No
Android App
No
Windows
No
Mac
No
Linux
No
Chromebook
No
Deployment
Web-Based
Yes
On-Premises
Yes
iPhone App
No
iPad App
No
Android App
No
Windows
No
Mac
No
Linux
No
Chromebook
No
Customer Support
Business Hours
Yes
Live Rep (24/7)
Yes
Online Support
Yes
Customer Support
Business Hours
No
Live Rep (24/7)
No
Online Support
Yes
Types of Training
Training Docs
Yes
Webinars
No
Live Training (Online)
Yes
In Person
Yes
Types of Training
Training Docs
Yes
Webinars
Yes
Live Training (Online)
Yes
In Person
No
Vendor Details
Company Name
Conviso Platform
Country
Brazil
Website
www.convisoappsec.com
Vendor Details
Company Name
Cycode
Founded
2019
Country
Israel
Website
cycode.com
Product Features
Application Security
Analytics / Reporting
No
Open Source Component Monitoring
No
Source Code Analysis
No
Third-Party Tools Integration
No
Training Resources
No
Vulnerability Detection
No
Vulnerability Remediation
No
Product Features
Application Security
Analytics / Reporting
No
Open Source Component Monitoring
No
Source Code Analysis
No
Third-Party Tools Integration
No
Training Resources
No
Vulnerability Detection
No
Vulnerability Remediation
No
Cybersecurity
AI / Machine Learning
No
Behavioral Analytics
No
Endpoint Management
No
IOC Verification
No
Incident Management
No
Tokenization
No
Vulnerability Scanning
No
Whitelisting / Blacklisting
No
DevOps
Approval Workflow
No
Dashboard
No
KPIs
No
Policy Management
No
Portfolio Management
No
Prioritization
No
Release Management
No
Timeline Management
No
Troubleshooting Reports
No
