Average Ratings 0 Ratings
Average Ratings 0 Ratings
Similar Products
-
Aikido SecurityAikido is the all-in-one security platform for development teams to secure their complete stack, from code to cloud. Aikido centralizes all code and cloud security scanners in one place. Aikido offers a range of powerful scanners including static code analysis (SAST), dynamic application security testing (DAST), container image scanning, and infrastructure-as-code (IaC) scanning. Aikido integrates AI-powered auto-fixing features, reducing manual work by automatically generating pull requests to resolve vulnerabilities and security issues. It also provides customizable alerts, real-time vulnerability monitoring, and runtime protection, enabling teams to secure their applications and infrastructure seamlessly.
-
AdvantageAdvantage is a superior subscription management system that allows you to order products and services with total flexibility. Flexibility allows you to run your business efficiently in the way that you want. You need a market-responsive order-to-cash solution to keep up with the increasing consumer preference for subscription and membership models.
-
JscramblerJscrambler is the leader in Client-Side Security, protecting the code, data, and digital interactions that power today’s modern web applications. Modern applications are changing rapidly as development teams adopt AI-generated code, rely on third-party software components, and embed AI-powered agents into digital experiences. Meanwhile, sensitive information is increasingly created and processed in the browser itself. This creates a critical gap in enterprise security: organizations need to govern not only what code enters an application, but how that code, scripts, and data behave when the application runs. Jscrambler closes that gap with a Client-Side Security Platform built around its Behavioral Enforcement Core. The platform continuously monitors and enforces how application code, including AI-generated code, third-party scripts, AI agents, and sensitive data behave in the browser. By enforcing software integrity and data governance at runtime, Jscrambler gives organizations control at the point where code executes and data is created—before sensitive information can be exposed or transmitted. Organizations across retail, financial services, travel, healthcare, and other industries use Jscrambler to detect and stop client-side attacks, protect against risks introduced by AI-developed and third-party code, control AI-driven data flows, and strengthen compliance with requirements including PCI DSS, GDPR, HIPAA, CIPA, CCPA, and the EU AI Act.
-
ParasoftParasoft's mission is to provide automated testing solutions and expertise that empower organizations to expedite delivery of safe and reliable software. A powerful unified C and C++ test automation solution for static analysis, unit testing and structural code coverage, Parasoft C/C++test helps satisfy compliance with industry functional safety and security requirements for embedded software systems.
-
GearsetGearset is a full‑featured Salesforce DevOps solution built for the enterprise, giving teams the tools to adopt best practices across every stage of the DevOps lifecycle. From metadata and CPQ deployments to CI/CD, testing, code analysis, sandbox seeding, backups, archiving, and observability, Gearset gives teams unmatched insight and control over their Salesforce workflows. Over 3,000 organizations — including names like McKesson and IBM — rely on Gearset to deliver with security and scale in mind. With advanced governance, detailed audit trails, SOX/ISO/HIPAA support, multi‑team pipelines, integrated security checks, and adherence to ISO 27001, SOC 2, GDPR, CCPA/CPRA, and HIPAA, Gearset combines enterprise‑ready compliance with rapid onboarding and an intuitive interface — all in one platform. Leading firms in finance, healthcare, and tech trust Gearset to power their DevOps initiatives without adding complexity.
-
FerootFeroot Security is a global leader in AI-powered website and web application compliance and security. Feroot AI protects digital experiences from hidden threats while continuously enforcing compliance with PCI DSS 4.0.1, HIPAA rules on online tracking technologies, CCPA/CPRA, GDPR, CIPA, and over 50 global laws and standards. The Feroot AI Platform replaces manual compliance work and operational overhead with continuous automation. What once required months of effort across security, engineering, and legal teams can now be deployed in minutes, delivering real-time protection and audit-ready evidence. Feroot unifies critical capabilities into a single platform, including JavaScript behavior analysis, web compliance scanning, third-party script monitoring, consent enforcement, and data privacy posture management. It is purpose-built to detect and stop web-based threats such as Magecart, formjacking, e-skimming, and unauthorized tracking on high-risk assets like payment pages, login flows, iframes, and healthcare portals. Trusted by Fortune 500 enterprises, healthcare providers, retailers, SaaS platforms, utilities, payment service providers, universities, and public sector organizations, Feroot safeguards hundreds of millions of users worldwide. Feroot AI solutions include PaymentGuard AI, HealthData Shield AI, AlphaPrivacy AI, CodeGuard AI, and MobileGuard AI. Visit feroot for more information.
-
Astra PentestAstra's Pentest is a comprehensive solution for penetration testing. It includes an intelligent vulnerability scanner and in-depth manual pentesting. The automated scanner performs 10000+ security checks, including security checks for all CVEs listed in the OWASP top 10 and SANS 25. It also conducts all required tests to comply with ISO 27001 and HIPAA. Astra provides an interactive pentest dashboard which allows users to visualize vulnerability analysis, assign vulnerabilities to team members, collaborate with security experts, and to collaborate with security experts. The integrations with CI/CD platforms and Jira are also available if users don't wish to return to the dashboard each time they want to use it or assign a vulnerability for a team member.
-
AnalyticsCreatorAnalyticsCreator is a metadata-driven design application for data warehouse automation and data product engineering across the Microsoft data stack. Its Governed Control Model connects business meaning, data structures, transformation rules, dependencies, lineage and technical implementation in one controlled project model. Data teams design the required architecture in AnalyticsCreator, then generate native Microsoft assets from that design. Generated outputs can include SQL Server objects, SSIS packages, Azure Data Factory pipelines, supported Microsoft Fabric components, deployment artefacts and Power BI semantic models. AnalyticsCreator supports dimensional, 3NF and hybrid modelling approaches together with ingestion, transformations, delta loading, historisation, Slowly Changing Dimensions, snapshots and repeatable data-processing patterns. Because generated outputs are native Microsoft technology, no AnalyticsCreator runtime is required in production. Organisations retain ownership of the resulting implementation and can integrate generated assets into Git, Azure DevOps and CI/CD workflows. Lineage, documentation and dependency information remain connected to the design, helping teams understand change impact before regenerating affected assets. Design Intelligence extends this governed project context into AI-assisted data engineering by providing authorised AI tools and agents with structured access to metadata, lineage, dependencies and design rules. Typical use cases include enterprise data warehouse development, Microsoft Fabric adoption, SQL Server and SSIS modernisation, governed Power BI delivery and repeatable data product engineering.
-
Airlock DigitalAirlock Digital delivers an easy-to-manage and scalable application control solution to protect endpoints with confidence. Built by cybersecurity professionals and trusted by organizations worldwide, Airlock Digital enforces a Deny by Default security posture to block all untrusted code, including unknown applications, unwanted scripts, malware, and ransomware.
-
Virtuoso QAVirtuoso QA is an AI-native test automation solution built to streamline and scale enterprise quality assurance processes. It allows users to author tests in natural language, making it accessible for both technical and non-technical team members. The platform leverages self-healing AI to automatically adapt to changes in applications, reducing test flakiness and maintenance overhead. With features like live authoring, real-time execution, and automated diagnostics, teams can quickly identify and resolve issues. Virtuoso QA supports continuous testing across multiple browsers, devices, and environments, ensuring comprehensive test coverage. It integrates seamlessly with popular tools such as Jira, Jenkins, Azure DevOps, and BrowserStack, enabling smooth CI/CD workflows. The platform also provides detailed analytics and dashboards to track performance and optimize testing strategies. By automating test generation and execution, it significantly reduces manual effort and accelerates release cycles. Virtuoso QA empowers organizations to deliver high-quality software faster and more reliably.
Description
Achieve detailed insight into engineering technologies, systems, and processes, all the way from the initial code to the final deployment. Effortlessly link Cider to your existing ecosystem while integrating security measures without disrupting engineering workflows. Enhance the security of your CI/CD pipeline by focusing on a customized set of prioritized risks and actionable recommendations suited to your specific environment. Cider flawlessly integrates with every component of your CI/CD process, delivering a thorough and precise evaluation of all technologies, frameworks, and integrations present in your setup. By mapping every intelligent connection in your environment, Cider offers complete visibility throughout the entire CI/CD journey, from source code management users to artifacts that are deployed in production. Evaluate the security posture of your engineering systems and processes comprehensively. Conduct an analysis of your environment against plausible attack scenarios to pinpoint necessary controls that will help minimize your CI/CD attack surface, ensuring a robust development cycle. This thorough assessment enables teams to proactively strengthen their defenses in an ever-evolving threat landscape.
Description
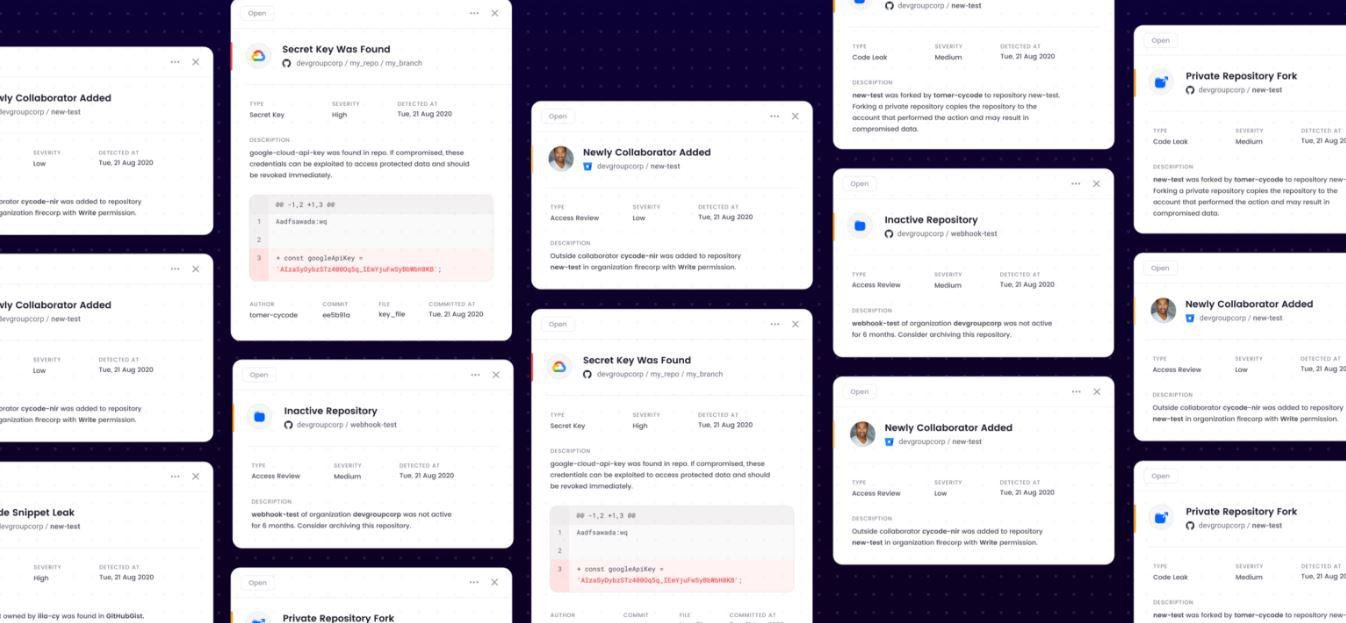
A comprehensive solution for ensuring security, governance, and pipeline integrity across all development tools and infrastructure is essential. Strengthen your source control management systems (SCM) by detecting secrets and leaks, while also safeguarding against code tampering. Examine your CI/CD configurations and Infrastructure-as-Code (IaC) for any security vulnerabilities or misconfigurations. Track any discrepancies between production systems’ IaC setups to thwart unauthorized code alterations. It's crucial to prevent developers from accidently making proprietary code public in repositories; this includes fingerprinting code assets and proactively identifying potential exposure on external sites. Maintain an inventory of assets, enforce stringent security policies, and easily showcase compliance throughout your DevOps ecosystem, whether it operates in the cloud or on-premises. Regularly scan IaC files for security flaws, ensuring alignment between specified IaC configurations and the actual infrastructure in use. Each commit or pull/merge request should be scrutinized for hard-coded secrets to prevent them from being merged into the master branch across all SCM platforms and various programming languages, thereby enhancing overall security measures. Implementing these strategies will create a robust security framework that supports both development agility and compliance.
API Access
Has API
No
API Access
Has API
No



Integrations
Amazon Web Services (AWS)
Yes
CircleCI
Yes
GitHub
Yes
GitLab
Yes
Jenkins
Yes
Kubernetes
Yes
Microsoft Azure
Yes
Rapyd
Yes
Terraform
Yes
AppsFlyer
Yes
Integrations
Amazon Web Services (AWS)
Yes
CircleCI
Yes
GitHub
Yes
GitLab
Yes
Jenkins
Yes
Kubernetes
Yes
Microsoft Azure
Yes
Rapyd
Yes
Terraform
Yes
AppsFlyer
No
Pricing Details
No price information available.
Free Trial
No
Free Version
No
Pricing Details
No price information available.
Free Trial
Yes
Free Version
No
Deployment
Web-Based
Yes
On-Premises
No
iPhone App
No
iPad App
No
Android App
No
Windows
No
Mac
No
Linux
No
Chromebook
No
Deployment
Web-Based
Yes
On-Premises
Yes
iPhone App
No
iPad App
No
Android App
No
Windows
No
Mac
No
Linux
No
Chromebook
No
Customer Support
Business Hours
No
Live Rep (24/7)
No
Online Support
Yes
Customer Support
Business Hours
No
Live Rep (24/7)
No
Online Support
Yes
Types of Training
Training Docs
Yes
Webinars
No
Live Training (Online)
Yes
In Person
No
Types of Training
Training Docs
Yes
Webinars
Yes
Live Training (Online)
Yes
In Person
No
Vendor Details
Company Name
Cider
Country
United States
Website
www.cidersecurity.io
Vendor Details
Company Name
Cycode
Founded
2019
Country
Israel
Website
cycode.com
Product Features
Application Security
Analytics / Reporting
No
Open Source Component Monitoring
No
Source Code Analysis
No
Third-Party Tools Integration
No
Training Resources
No
Vulnerability Detection
No
Vulnerability Remediation
No
Product Features
Application Security
Analytics / Reporting
No
Open Source Component Monitoring
No
Source Code Analysis
No
Third-Party Tools Integration
No
Training Resources
No
Vulnerability Detection
No
Vulnerability Remediation
No
Cybersecurity
AI / Machine Learning
No
Behavioral Analytics
No
Endpoint Management
No
IOC Verification
No
Incident Management
No
Tokenization
No
Vulnerability Scanning
No
Whitelisting / Blacklisting
No
DevOps
Approval Workflow
No
Dashboard
No
KPIs
No
Policy Management
No
Portfolio Management
No
Prioritization
No
Release Management
No
Timeline Management
No
Troubleshooting Reports
No
